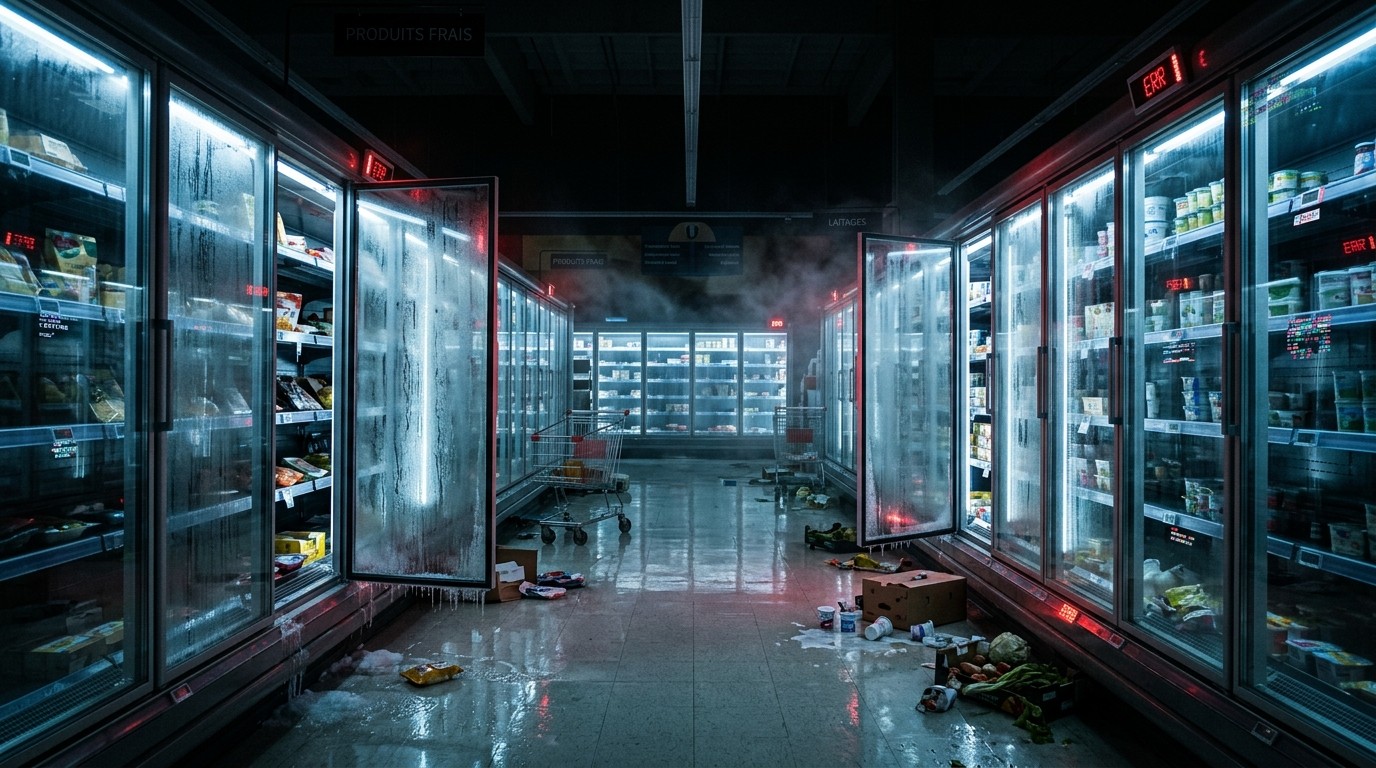

I still remember walking into a local grocery store last winter and hearing the low hum of the refrigeration units working overtime. That steady sound has always felt reassuring, a quiet guarantee that the milk, meat and produce would stay safe. Now imagine that hum turning into something else entirely. Across France, hundreds of supermarket refrigeration systems were recently forced into chaotic operating modes by a remote cyberattack. Temperatures climbed, ice melted, and entire sections of perishable stock became unsellable almost overnight. The episode feels less like a typical data breach and more like someone reaching into the physical world through a digital door.
When Connected Equipment Becomes a Liability
Modern supermarkets rely on networks of sensors, controllers and remote management platforms to keep everything from frozen pizza to fresh fish at the right temperature. These systems save energy and labor, yet they also create new pathways for interference. In this case the attackers did not appear interested in customer payment data or loyalty-program details. Their focus stayed on the refrigeration units themselves. By altering set points and forcing continuous defrost cycles, they turned ordinary cooling equipment into agents of destruction.
Reports indicate that roughly 150 to 200 Intermarché locations and nearly 100 Coopérative U stores experienced the disruption. E. Leclerc, the country’s largest supermarket operator, was also affected, while other well-known chains faced possible involvement. In some stores the internal temperature of display cases reportedly climbed toward 122°F. That is not a mild malfunction. That is a deliberate push past the point where food safety standards can be met.
The Scale of Immediate Physical Damage
Two stores in Alsace alone recorded combined losses near €270,000. Multiply that figure across hundreds of locations and the financial impact becomes substantial. Spoiled inventory is only the first layer. Some refrigeration units themselves may have suffered lasting harm after being driven into abnormal operating ranges for extended periods. In a few instances equipment reportedly overheated to the point of catching fire, adding another dimension of risk that no retailer wants to confront.
I’ve found that people outside the industry sometimes underestimate how quickly perishable goods lose value once temperature control slips. A single overnight incident can erase an entire week’s margin on dairy, meat and prepared foods. When the same problem hits dozens or hundreds of stores simultaneously, the cumulative effect stretches far beyond any one balance sheet.
This kind of incident is unlike anything the industry had previously experienced.
That assessment from a senior retail executive captures the unsettled mood. Traditional cyber defenses were built around data protection and ransomware recovery. They were never designed to stop someone from turning a freezer into a slow cooker.
How Attackers Gained Control Without Stealing Data
The precise technical pathway remains under investigation, yet the outcome is clear. Temperature controls were altered remotely. Continuous defrost modes were activated. Set points were driven far outside safe ranges. These actions require access to the industrial control layer that sits behind everyday building-management software. Once that layer is compromised, the physical consequences unfold automatically.
What makes the episode particularly unsettling is the apparent absence of a ransom demand. Many high-profile attacks begin with encryption of systems followed by payment requests. Here the goal seemed to be straightforward destruction of inventory and possible damage to hardware. That shift in motive changes the calculus for every company that depends on connected equipment.
- Remote alteration of temperature set points
- Forced continuous defrost cycles lasting hours
- Abnormal heating of refrigeration components
- Rapid spoilage of large volumes of perishable stock
- Secondary risk of equipment fire or permanent failure
Each of those outcomes can be triggered without ever stepping inside a store. The only requirement is sufficient access to the networked controllers that modern retailers increasingly depend upon.
Broader Implications for Everyday Commerce
Supermarkets sit at the intersection of food supply, local employment and daily consumer routines. When cooling systems fail en masse, the disruption is felt immediately by shoppers who find empty shelves or closed sections. Staff must scramble to discard spoiled product, document losses and restore safe operating conditions. Insurance questions arise almost as quickly as the first spoiled packages are pulled from the cases.
In my view the most lasting effect may be the quiet recalculation of risk that is now happening inside boardrooms. For years the conversation around cyber security focused on customer data and payment systems. The French incident demonstrates that industrial control systems inside ordinary retail locations can become weapons against the physical inventory those same systems were meant to protect.
Retailers now face a dual challenge. They must keep the energy-saving benefits of connected equipment while hardening the pathways that allow remote interference. That balance is harder than it sounds. Many older refrigeration controllers were never designed with sophisticated authentication in mind. Upgrading them across hundreds of stores is expensive and operationally complex.
Insurance, Recovery and the Question of Coverage
After the immediate clean-up comes the paperwork. Claims will need to document the exact sequence of temperature excursions, the volume of product discarded, and any permanent damage to compressors or control boards. Some policies may treat the event as a cyber incident, others as a form of vandalism or equipment failure. The distinction matters when millions of euros are at stake.
Recovery also involves restoring trust in the systems themselves. Store managers need confidence that another remote override will not occur the following week. That confidence requires both technical fixes and clear communication from corporate security teams. Until those steps are complete, every unexpected temperature alarm will carry extra weight.
Why This Incident Feels Different From Earlier Cyber Events
Most publicized cyberattacks still center on data. Customer records are stolen, systems are locked with ransomware, or websites are taken offline. Those events are disruptive and expensive, yet they usually leave the physical operation of a store intact. Shelves can still be restocked. Refrigerators continue to run. Customers can still walk the aisles.
This time the attack jumped the boundary. Digital commands produced measurable physical harm. Food that should have remained safe became hazardous. Machinery that should have cooled instead generated heat. The gap between bits and atoms narrowed in a way that few retailers had prepared for.
Perhaps the most interesting aspect is how ordinary the target appeared. These were not power plants or water-treatment facilities. They were neighborhood supermarkets. The same logic that protects critical national infrastructure now needs to extend to the everyday systems that keep milk cold and frozen vegetables solid.
Lessons Emerging for the Wider Retail Sector
Other chains are almost certainly reviewing their own remote-management platforms right now. Segmentation between corporate networks and store-level industrial controllers is receiving fresh attention. Multi-factor authentication for any system that can change temperature set points is moving higher on priority lists. Continuous monitoring for anomalous commands is no longer optional.
I’ve noticed that conversations among security professionals have shifted in tone. The earlier focus on preventing data exfiltration remains important, yet a second track has opened: preventing the conversion of operational technology into a tool of physical sabotage. That dual mandate requires skills that many traditional IT teams do not yet possess in depth.
- Map every device that can influence temperature or humidity inside stores
- Isolate those devices from general corporate networks wherever possible
- Require strong authentication before any remote configuration change
- Log and alert on unusual command sequences in real time
- Test recovery procedures that assume simultaneous multi-store failure
Those five steps sound straightforward on paper. Implementing them across a national footprint of stores is a multi-year program. Yet the cost of inaction has now been demonstrated in concrete terms.
The Human Cost Behind the Spoiled Inventory
Behind the financial figures sit store teams who arrived for their shifts and discovered melting freezers and the smell of spoiled product. Cleaning up after such an event is unpleasant and time-consuming. Staff must discard large volumes of food, document every loss for insurance, and still try to keep the rest of the store functioning for customers. Morale takes a hit when hard work is undone by an invisible intrusion.
Customers feel the effect too. Empty dairy cases or closed meat counters disrupt weekly shopping routines. In smaller towns a single large supermarket may be the primary source of fresh food. Temporary shortages create genuine inconvenience and, in some cases, genuine hardship for households that rely on predictable access to refrigerated goods.
In my experience these secondary effects are often overlooked in the first wave of reporting. The dramatic image of melting freezers captures attention, yet the quieter strain on employees and local communities lasts longer.
Looking Ahead: Hardening Everyday Infrastructure
The French authorities have opened a criminal investigation. Prosecutors are examining the full scale of losses and the reports of equipment fires. Attribution remains unsettled. No public evidence has yet pointed to a specific group or nation-state. That uncertainty itself is part of the new reality. When attacks can be launched from anywhere and leave limited forensic footprints, traditional notions of deterrence become harder to apply.
What is clearer is the trajectory. Connected industrial equipment is spreading through every sector of the economy. The same convenience that allows a technician to adjust a freezer from a central office also allows an adversary to do the same. Closing that gap will require sustained investment, better design standards, and a willingness to treat operational technology with the same seriousness once reserved for core IT systems.
Retailers that treat this episode as a one-off anomaly risk repeating the same experience. Those that treat it as an early warning have an opportunity to strengthen their defenses before the next wave arrives. The choice is no longer theoretical. The melting freezers in French stores have already made the stakes visible.
I keep returning to that quiet hum of a well-functioning refrigeration unit. It used to feel like background noise. After this incident it sounds more like a reminder. Every connected system that keeps modern life convenient also carries the potential to disrupt that same life when the wrong hands gain control. The challenge now is to keep the convenience while removing the vulnerability. That work has only just begun.
Practical Steps Retailers Can Take Immediately
Even before full system redesigns are complete, several practical measures can reduce exposure. First, limit remote access to temperature controllers to a small number of verified accounts. Second, require out-of-band confirmation for any change that pushes set points outside normal ranges. Third, install independent temperature loggers that alert staff when primary controllers report values that diverge from reality. These steps will not eliminate every risk, yet they raise the difficulty for anyone attempting a similar intrusion.
Staff training also matters. Employees who understand the difference between a normal compressor cycle and an abnormal defrost command can serve as an early warning layer. Simple observation still has value even in a highly automated environment.
Finally, scenario planning should expand beyond traditional ransomware. Exercises that simulate simultaneous loss of cooling across multiple stores will reveal gaps in response playbooks that pure data-focused drills never uncover.
The Quiet Expansion of Hybrid Threats
Some observers have noted the broader context of heightened concern about foreign interference targeting essential services. Whether or not this particular incident fits that pattern remains unconfirmed. What is confirmed is the technical feasibility of turning everyday commercial equipment into a vector for disruption. That feasibility alone changes the threat landscape for any organization that operates large numbers of networked physical systems.
The line between cyber security and physical security continues to blur. Protecting one without the other is no longer sufficient. Retailers, logistics firms, and food distributors all share exposure to this new class of risk. Coordinated attention across those sectors will be needed if the next incident is to be smaller rather than larger.
In the end the French supermarket episode serves as a concrete illustration rather than an abstract warning. Real stores lost real inventory. Real equipment may have been permanently damaged. Real employees spent long hours cleaning up the consequences. Those facts make the conversation about securing connected refrigeration systems less theoretical and far more urgent.
The path forward will involve better technology, clearer standards, and a cultural shift that treats operational technology with the seriousness it now requires. Until that shift is complete, the quiet hum of a supermarket freezer will carry a faint undercurrent of vulnerability that was harder to hear before this attack made the risk impossible to ignore.