

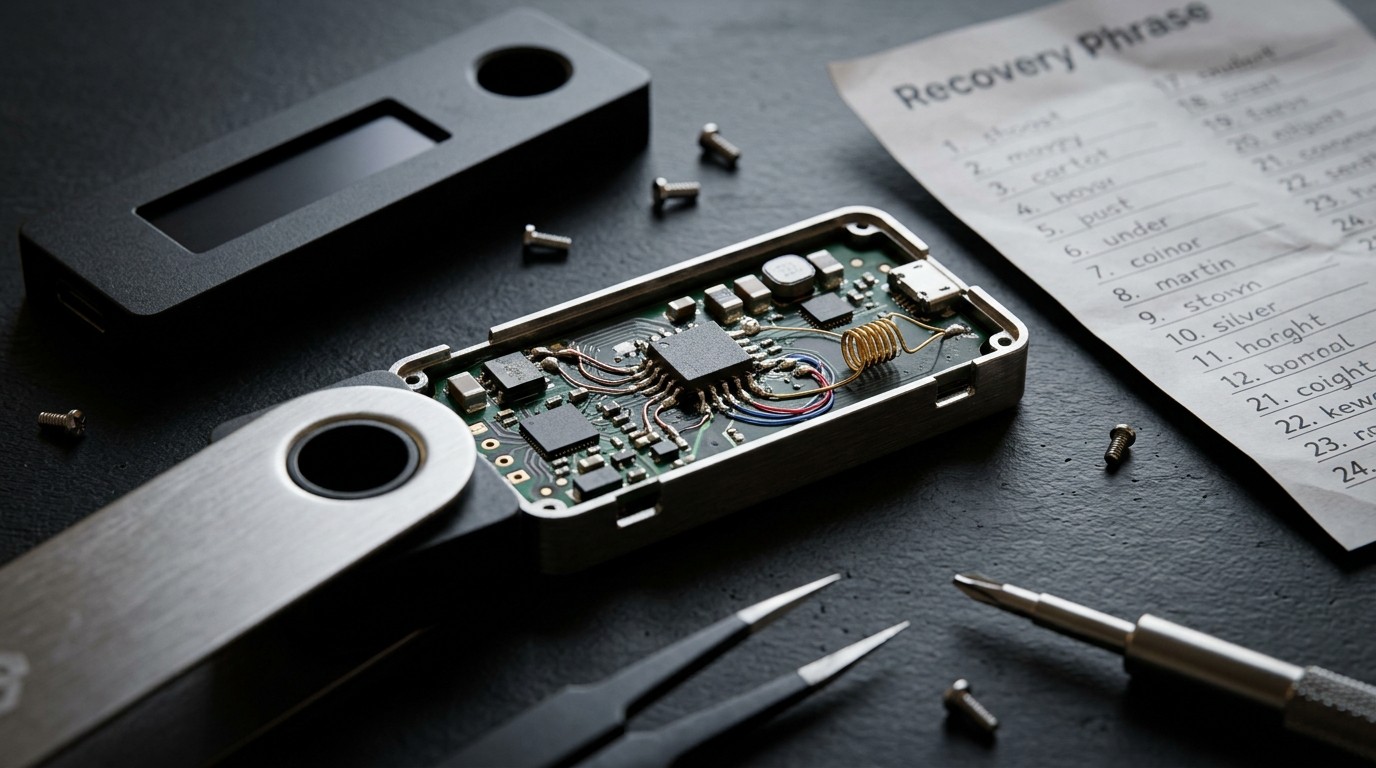

I still remember the first time I set up a hardware wallet. Sitting at my kitchen table, carefully writing down those twenty-four words, I felt a quiet sense of control. Those phrases were the only keys to everything I had worked for. Now imagine discovering that a tiny piece of circuitry, slipped inside the device before it ever reached your hands, had been watching that exact moment and sending the words out into the world. That is no longer a hypothetical fear. It is the reality Ledger has confirmed in a recent investigation that has left many holders shaken.
How A Hidden Implant Quietly Captured Recovery Phrases
The story began with reports of missing funds. Customers who had bought certain devices through a Southeast Asian reseller started noticing balances vanishing. Ledger’s security researchers moved quickly. What they found inside one of the returned units was not a software flaw or a clever phishing trick. It was physical hardware that should never have been there.
An unauthorized component sat inside the casing. It monitored the screen during the critical setup process. When the familiar recovery phrase screens appeared, the implant’s microcontroller read the displayed words, decoded them, and transmitted the information through an LTE connection powered by a provisioned eSIM. The whole operation happened independently of the wallet’s normal security systems.
What makes this particularly unsettling is that the implant left the Secure Element untouched. It did not rewrite the operating system, alter transactions, or forge signatures. It simply watched the display and listened for the moment when the most sensitive information appeared in plain text. In my view, that approach is almost more alarming than a direct attack on the chip that holds private keys. It shows how a determined actor can bypass layers of protection by targeting the human interface instead.
What The Investigation Has Confirmed So Far
Ledger’s Donjon team verified the presence of the implant on one affected customer’s device. Every fund loss the company has been able to confirm so far traces back to units sold through the same reseller. That reseller has since suspended sales of the devices while the examination continues.
Independent blockchain analysis has pointed to larger numbers. One firm estimated movements linked to the incident across hundreds of wallets, with totals reaching into the tens of millions. Ledger itself has been careful not to endorse those figures. The company has stated it has not verified the total number of affected users or the overall value lost. Third-party calculations, it notes, remain unverified.
This measured tone is understandable. Jumping to conclusions in a case involving physical tampering can create more confusion than clarity. Still, the core technical finding is solid: the implant works by reading the screen and sending data over a cellular network. That detail alone changes how many of us will think about the supply chain from now on.
Why The Secure Element Was Left Alone
Hardware wallets are built around the idea that the most sensitive operations stay inside a protected chip. The Secure Element is designed to resist physical probing and keep private keys isolated. Attackers who want to extract those keys usually face a high bar.
The implant sidestepped that problem entirely. By focusing on the recovery phrase shown during initial setup, it harvested the one piece of information that can recreate the entire wallet elsewhere. Once those twenty-four words leave the device, the original hardware becomes almost irrelevant. An attacker can generate the same keys on any other machine.
I find this detail especially instructive. It reminds us that security is only as strong as its weakest visible moment. The screen that displays the recovery phrase is a necessary step for legitimate users, yet it is also an open window if the wrong component is watching.
The Role Of The Reseller And The Supply Chain Question
All confirmed cases so far involve devices purchased through one specific reseller serving Southeast Asian markets. That fact has focused attention on how the implants entered the units. Ledger has not yet determined the exact point of insertion or identified those responsible. No arrests or formal charges have been announced.
The reseller acted promptly once the investigation began, stopping sales and cooperating with the review of affected stock. That response is important. Yet the broader question remains: how many other devices might carry similar modifications, and how far back in the chain did the tampering occur?
Ledger has stated it has not verified any drain linked to a signer bought through other channels. Researchers continue to examine reports involving hardware modifications in other locations. For now, the evidence points to a localized problem rather than a company-wide compromise of the manufacturing process.
Still, anyone who has ever ordered a hardware wallet online will feel a new layer of caution. Packaging can look intact. Seals can appear unbroken. A sophisticated implant can hide beneath the surface and activate only when the recovery phrase appears.
Immediate Steps For Anyone Who Bought Through The Affected Channel
Ledger has issued clear guidance. If you purchased a device through the reseller in question and have not yet initialized it, do not set it up. Contact official support first. Opening the packaging and generating a recovery phrase could expose the words immediately.
Those who have already used an affected device face a different urgency. The company advises moving funds without delay to a new wallet that has been initialized with an entirely fresh recovery phrase. Importing the old phrase into another unit from the same reseller would simply transfer the risk.
- Transfer remaining assets to a newly generated recovery phrase on a verified device
- Never reuse the original twenty-four words
- Report any confirmed losses through official support channels
- Contact local law enforcement if funds are missing
- Do not open or ship the hardware without first speaking to support or authorities
The last point matters more than it might seem. Physical evidence can be crucial in an investigation. Opening the casing without proper handling risks contaminating that evidence or damaging components that researchers still need to examine.
Ledger has also reminded users that it will never call customers, send unsolicited messages, or ask for recovery phrases. Separate phishing campaigns have appeared around the same time, but no direct link to the hardware incident has been established. The coincidence is still worth noting. When fear rises, opportunistic scams often follow.
What The Technical Details Reveal About Future Risks
The implant’s design is elegant in a disturbing way. A separate microcontroller watches the display. When it recognizes recovery phrase screens, it captures the data and pushes it out over cellular networks. The eSIM provides connectivity without needing the user to notice any unusual behavior. The wallet continues to function normally for everyday signing operations.
Because the Secure Element and the operating system remain intact, routine checks that look only at software integrity would miss the problem. Physical inspection becomes the only reliable way to detect such an implant, and even then the component can be small enough to require careful examination under proper lighting and tools.
In my experience following hardware security stories, this kind of attack sits in a different category from remote exploits. It requires physical access at some point in the supply chain. That barrier is higher, yet once cleared, the payoff can be substantial and the detection window longer.
Researchers are still analyzing additional devices as they arrive. More details will likely emerge about the exact components used, the cellular network activity, and any patterns that might point to the origin of the modifications. For the moment, the public findings already give a clear picture of the method.
Broader Lessons For Hardware Wallet Owners
Most of us buy hardware wallets precisely because we want to remove private keys from internet-connected computers. The assumption is that the device itself arrives clean and stays that way. This incident challenges that assumption in a concrete way.
Buying from authorized channels remains the strongest practical defense. Yet even authorized resellers can, in rare cases, become points of compromise. Visual inspection of packaging helps, but sophisticated tampering can defeat casual checks. Some users may now consider generating recovery phrases in controlled environments or using multi-signature setups that reduce the impact of a single compromised phrase.
Another practical step is to treat any unexpected loss of funds as a potential hardware issue until proven otherwise. Software wallets and exchange accounts produce different forensic trails. When the trail points back to a physical device purchased through a specific route, the possibility of an implant should enter the conversation early.
I have always believed that the best security practices combine technical controls with healthy skepticism about the physical path a device has traveled. This case reinforces that view.
How The Investigation Continues
Ledger’s research team specializes in physical and logical attacks against signing devices. Their ongoing work includes circuit analysis, component inspection, and testing of the mechanisms that protect private keys. Additional units submitted by customers will expand the sample size and may reveal whether the implant design varied across different batches.
The company has invited researchers and others who may hold relevant evidence to share findings through official channels. Affected customers are directed to support for personalized guidance. No timeline has been set for a final report. In investigations of this type, patience is usually wiser than speed. Incomplete information can create false reassurance or unnecessary panic.
One aspect worth watching is whether similar implants appear in devices sold through other routes. Ledger has been explicit that it has not verified such cases so far. Continued monitoring of reports from different regions will determine whether the problem stays contained or points to a wider pattern.
Practical Advice Beyond The Immediate Response
For users who obtained their devices through other channels, inspection guidance is available. Opening a hardware wallet can damage it, so any physical check should only happen after the recovery phrase is securely backed up and funds have been moved if necessary. The risk of accidental damage is real, and the benefit of opening a unit that shows no signs of compromise may be limited.
A more lasting habit is to keep recovery phrases offline and never photograph or store them on any connected device. That practice does not prevent an implant from capturing the words during setup, but it does reduce secondary exposure risks that often accompany careless handling of the phrase later.
Multi-signature arrangements offer another layer of protection. Even if one recovery phrase is compromised, an attacker still needs additional keys controlled by separate devices or parties. The setup is more complex, yet for larger holdings the trade-off can be worthwhile.
Perhaps the most interesting aspect of this whole episode is how it forces a recalibration of trust. We trust the manufacturer to design secure hardware. We trust the packaging to arrive sealed. We trust the reseller to handle inventory carefully. When any link in that chain fails, the consequences can be severe and hard to reverse.
Understanding The Difference Between Confirmed And Estimated Losses
Numbers circulating online have varied. Independent analysis has suggested figures around one hundred million across several hundred wallets. Ledger has deliberately avoided confirming those totals. The distinction is important. Blockchain tracing can identify suspicious movements, but linking every transaction to a specific hardware implant requires additional evidence that may not yet exist for every case.
Some drains might stem from other causes entirely: phishing, social engineering, or malware on a connected computer. Separating those incidents from the hardware implant cases takes time and careful verification. Overstating the scale can create panic; understating it can leave victims without the urgency they need. The current public stance tries to stay between those extremes.
For individuals who believe they may be affected, the practical path remains the same regardless of the headline numbers. Move funds to a fresh recovery phrase on a clean device, report the incident, and preserve the original hardware for examination if requested.
Why This Incident Feels Different From Past Security Stories
Most previous hardware wallet concerns have centered on theoretical attack surfaces or rare software vulnerabilities. This case involves confirmed physical modification of devices that reached customers. The implant performed its task during normal setup and used cellular connectivity to exfiltrate data without any user interaction beyond the ordinary initialization steps.
That combination is rare. It demonstrates both the ingenuity of the attackers and the difficulty of detecting such modifications through software-only means. It also highlights the value of specialized security research teams that can open devices, examine circuitry, and reconstruct the behavior of unknown components.
I have followed enough security incidents to know that each one eventually becomes a case study for the next generation of defenses. Manufacturers will likely review packaging, sealing methods, and reseller agreements. Users will ask more questions about the origin of their devices. Researchers will look for similar implants in other product lines. The long-term effect may be a quieter, more careful approach to the entire supply chain.
Final Thoughts On Protecting What Matters
The recovery phrase remains the single most powerful piece of information associated with a cryptocurrency wallet. Everything else—the hardware, the software, the network connections—exists to protect or use that phrase. When an implant can capture it at the exact moment it first appears, the rest of the security model is temporarily bypassed.
Ledger’s findings give the community a concrete description of how that capture occurred in this instance. The company has provided practical steps for those who may be affected and continues to examine the physical evidence. Independent researchers have offered their own estimates of scale. The full picture is still forming.
For the rest of us, the episode is a reminder that physical security and supply-chain integrity deserve the same attention we already give to software updates and phishing awareness. A tiny chip hidden inside a trusted device can undo years of careful self-custody if the recovery phrase is exposed at the wrong moment.
Stay cautious about where devices are purchased. Treat any unexplained loss of funds with urgency. Keep recovery phrases offline and never reuse them once exposure is suspected. And remember that official support channels exist for a reason—use them when something feels wrong.
The investigation is not finished. More details will surface. Until then, the practical advice is straightforward: if your device came through the affected channel, act on the guidance already issued. If it did not, remain alert but avoid unnecessary panic. Security is rarely perfect. The best we can do is stay informed, move quickly when evidence appears, and keep refining the habits that protect the keys we cannot afford to lose.



