
Have you ever bought a hardware wallet thinking it was the ultimate safe haven for your crypto, only to wonder later if the device itself could be the weak link? That uneasy feeling just got a lot more real for people shopping in Germany. As of mid-October, one major electronics retailer has completely stopped selling Ledger devices both in stores and online, and the company behind the wallets agreed to the move while a probe into a reported implant continues.
No customer funds disappeared in the German case itself, according to the latest updates. Still, the decision to pull products from shelves sends a clear signal that something serious enough is under the microscope. I have been following hardware wallet stories for years, and this one stands out because it hits right at the retail channel most everyday buyers trust.
What Triggered the Sudden Sales Freeze in Germany
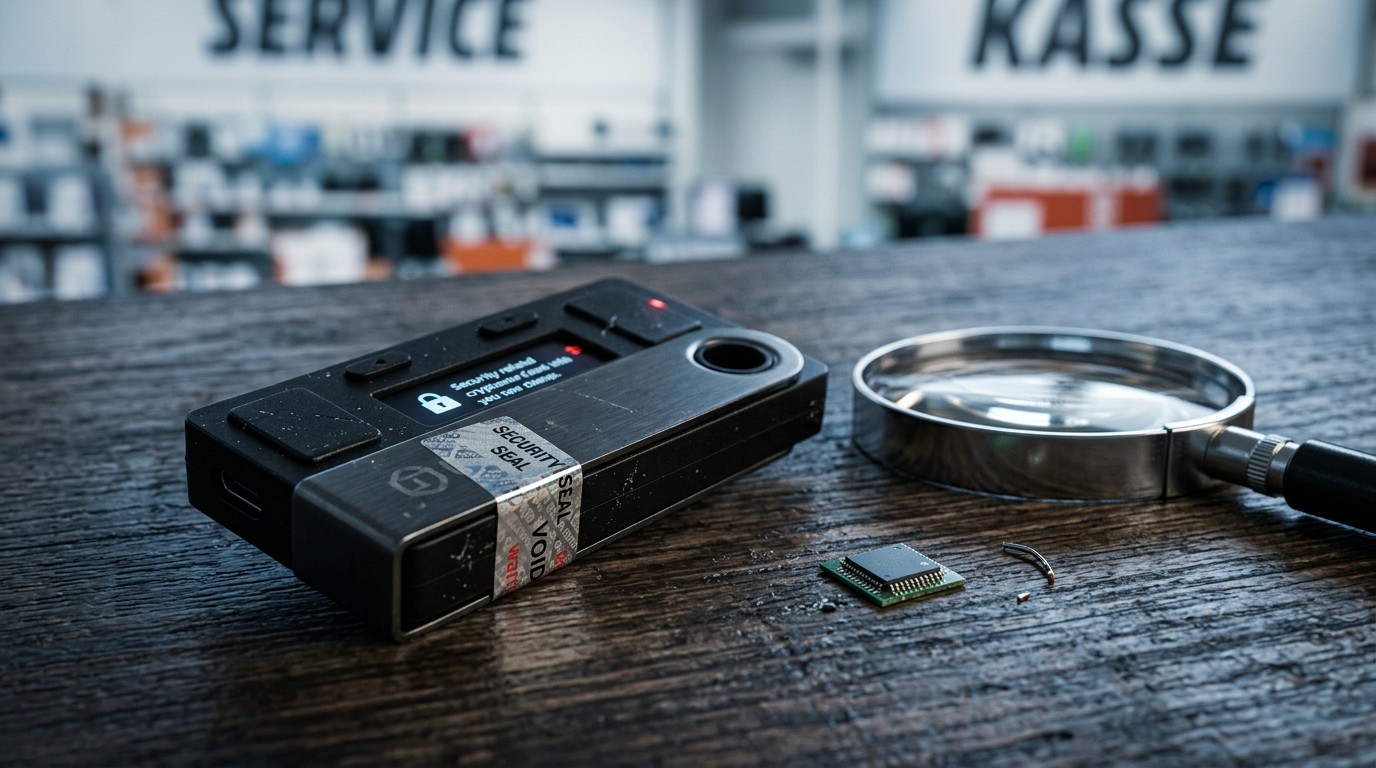
A single customer report started the chain of events. Someone in Germany claimed their Ledger device arrived with an unexpected implant. The retailer, a well-known electronics chain, reacted by suspending every Ledger hardware wallet from both physical stores and its online shop. Ledger itself aligned with that choice while its security team digs deeper.
The suspension covers the full range of devices available through that channel. No official timeline has been given for when sales might restart. The company also stayed quiet on exactly how many units might need checking or which specific model was involved in the report.
What matters most right now is the absence of confirmed fund losses tied to this particular German incident. Ledger stated clearly that its own infrastructure, systems, and services show no signs of compromise. That distinction feels important. The problem, if real, appears limited to a physical device modification rather than a company-wide breach.
How the Investigation Is Unfolding
Ledger’s internal security research group, known for stress-testing its own products, will examine any devices sent in. Support staff are already reviewing incoming customer messages. The company asked anyone with concerns about a recently purchased unit to reach out through official channels only.
Scammers love moments like this. Ledger issued a firm reminder that its team will never call you, send unexpected private messages, or request your 24-word recovery phrase. Anyone asking for those words is almost certainly trying to drain your account.
In my view, that warning might be the most practical piece of advice in the whole statement. Panic creates openings for social engineering, and recovery phrases remain the single most valuable piece of information a thief can obtain.
The Earlier Case That Raised the Stakes
Just hours before the German announcement, details emerged about a separate but related investigation. Modified devices had been sold through a Southeast Asian reseller. Researchers confirmed that an unauthorized component inside those units could capture recovery phrases during the initial setup process.
The implant relied on a separate microcontroller and an eSIM module. It watched the screen while the recovery words appeared, then transmitted them over a cellular connection. Importantly, the core Secure Element, the operating system, and the transaction signing process stayed untouched. From the outside the device looked and behaved normally.
Complaints about missing funds from customers of that reseller began arriving around the same time. Blockchain data later suggested losses in the neighborhood of one hundred million dollars across hundreds of wallets, though Ledger has not verified the exact figure or confirmed that every suspicious movement stemmed from the modified devices.
What the company did confirm is that every verified loss it examined involved hardware bought through that specific reseller. No confirmed thefts have been tied so far to devices purchased through other channels.
Why Third-Party Retail Channels Suddenly Feel Riskier
Most people buy hardware wallets because they want to keep private keys offline. The entire security model rests on the assumption that the device itself has not been tampered with before it reaches your hands. When that assumption cracks, even slightly, confidence takes a hit.
Retail stores and online marketplaces add layers of handling. Devices sit on shelves, move through warehouses, and pass through multiple hands. An implant small enough to hide inside a compact device can theoretically be added at any of those points. Detecting it without opening the case or running specialized tests is nearly impossible for an average buyer.
Ledger has long recommended buying directly or through carefully vetted partners. The current situation shows why that advice exists. Even a reputable electronics chain can become an unexpected vector if supply-chain controls slip somewhere along the way.
Practical Steps for Anyone Who Owns a Ledger Right Now
If you bought your device from an authorized source and it has been working without issues, the risk remains low based on current information. Still, a few habits are worth reinforcing.
- Never share your recovery phrase with anyone, for any reason
- Ignore unsolicited messages claiming to be from support
- Consider moving funds to a freshly initialized device if you have any lingering doubts about the original purchase channel
- Keep the recovery phrase offline and in a secure physical location
- Update the device firmware only through official methods
Restoring an old recovery phrase onto a new device will not help if that phrase was already captured during the first setup. The phrase itself is the vulnerability in these implant scenarios.
I have always treated the moment of first initialization as the most critical. Watching the screen carefully, verifying that no extra hardware is attached, and generating the phrase in a private setting still feels like the best first line of defense.
The Broader Supply Chain Question No One Likes Discussing
Hardware wallets sit at an interesting intersection. They are physical objects manufactured, shipped, and sold like any other electronics product. At the same time they hold the keys to digital assets that can be moved irreversibly in seconds. That combination creates unique pressure on every step of the logistics chain.
Manufacturers invest heavily in secure elements and tamper-resistant designs. Yet once the finished product leaves the factory, control becomes distributed. Resellers, distributors, and retail staff all become potential points of exposure. Most of the time the system works. Occasionally it does not.
The German suspension and the earlier reseller case both illustrate how quickly trust can erode. Even when the manufacturer’s own systems remain intact, the perception of risk spreads fast. Retail partners understand that perception. Pulling products from shelves is often the fastest way to limit damage while facts are still being established.
What Ledger Has Confirmed and What Remains Unknown
Several points are clear at this stage. No funds were lost in the specific German report that prompted the sales freeze. Ledger’s core infrastructure shows no evidence of compromise. The company’s security researchers are examining devices and customer reports. Sales through the affected German retailer remain paused with no restart date announced.
Open questions include the exact nature of the reported implant, whether it shares any technical similarities with the earlier modified devices, and how many units across different channels might eventually require closer inspection. Ledger has said it will release more information as the investigation advances.
Online speculation has already produced a range of unverified claims. The company specifically cautioned against treating those circulating numbers and stories as established fact. That measured tone feels appropriate while the technical work continues.
Phishing Attempts Riding the Wave of Bad News
Whenever a security story gains attention, fraudulent websites and ads tend to multiply. Recent weeks already saw fake pages designed to look like official Ledger verification portals. Some appeared in search results and directed users toward malicious wallet applications that harvested recovery phrases.
These phishing efforts appear separate from the hardware implant investigations. They simply exploit the moment of heightened anxiety. The advice stays consistent: type the official address yourself, never click links from unexpected messages, and treat any request for a recovery phrase as a red flag.
Perhaps the most interesting aspect is how quickly opportunistic attackers adapt. A single report of a possible implant becomes the social-engineering hook for a completely different attack vector. Staying calm and sticking to established security habits remains the most effective countermeasure.
Why Hardware Wallets Still Matter Despite These Incidents
It is easy to feel discouraged when stories like this surface. Yet the alternative of keeping large amounts of crypto on exchange platforms or in software wallets connected to the internet carries its own well-documented risks. Hardware devices, when genuine and properly handled, still remove private keys from online environments.
The current cases highlight a different category of threat: physical supply-chain interference rather than remote software attacks. That threat is real but also narrower. It tends to affect specific batches or specific resellers rather than every device in circulation.
Buying from the most direct and transparent channel possible, verifying packaging integrity, and generating recovery phrases in controlled conditions continue to reduce exposure. No security tool is perfect. The goal is always to make successful attacks significantly harder and more expensive for the adversary.
Looking Ahead: What Could Change After This Probe
Retail partners may tighten receiving and inventory procedures. Manufacturers might introduce additional visual or electronic authentication features that are harder to forge. Buyers could become more selective about purchase channels and more willing to pay a premium for direct fulfillment.
I suspect we will also see more public discussion about the limits of physical security. A device can contain a highly secure chip and still be vulnerable if an attacker adds a secondary component that observes user interaction during setup. Solving that problem may require changes in both design and distribution.
For now the practical focus stays on the investigation itself. Ledger has committed to sharing further findings. The German retailer has paused sales while that work continues. Customers who feel uneasy have clear paths for contacting support and, if necessary, migrating assets to new devices.
A Personal Note on Trust and Cold Storage
Over the years I have watched hardware wallet technology mature from niche enthusiast tools into mainstream products. That growth brought better interfaces, stronger chips, and wider availability. It also brought the inevitable attention of sophisticated attackers looking for any weak point.
The German sales suspension is a reminder that security is a process rather than a finished product. Even the most carefully engineered device can face new challenges once it enters the physical world of warehouses and retail floors. Transparency during investigations helps restore confidence faster than silence ever could.
If you hold crypto on a hardware wallet, take a moment this week to review where you bought it, how you stored the recovery phrase, and whether any recent messages about the device seem off. Small checks performed calmly beat rushed reactions every time.
The story is still developing. More technical details will likely surface in the coming days or weeks. Until then the smartest stance combines caution with measured action rather than panic. Your keys, your responsibility remains true, and that responsibility includes staying informed about how the devices themselves reach your hands.
Hardware wallets were never magic. They are tools that shift risk away from always-online environments. When those tools face supply-chain questions, the honest response is to examine the questions carefully, improve the processes that need improving, and keep the broader security model intact. That work is underway right now in Germany and beyond.
Stay patient, verify everything through official channels, and treat your recovery phrase like the irreplaceable secret it is. The investigation will run its course. In the meantime the best protection is the same set of disciplined habits that made hardware wallets valuable in the first place.