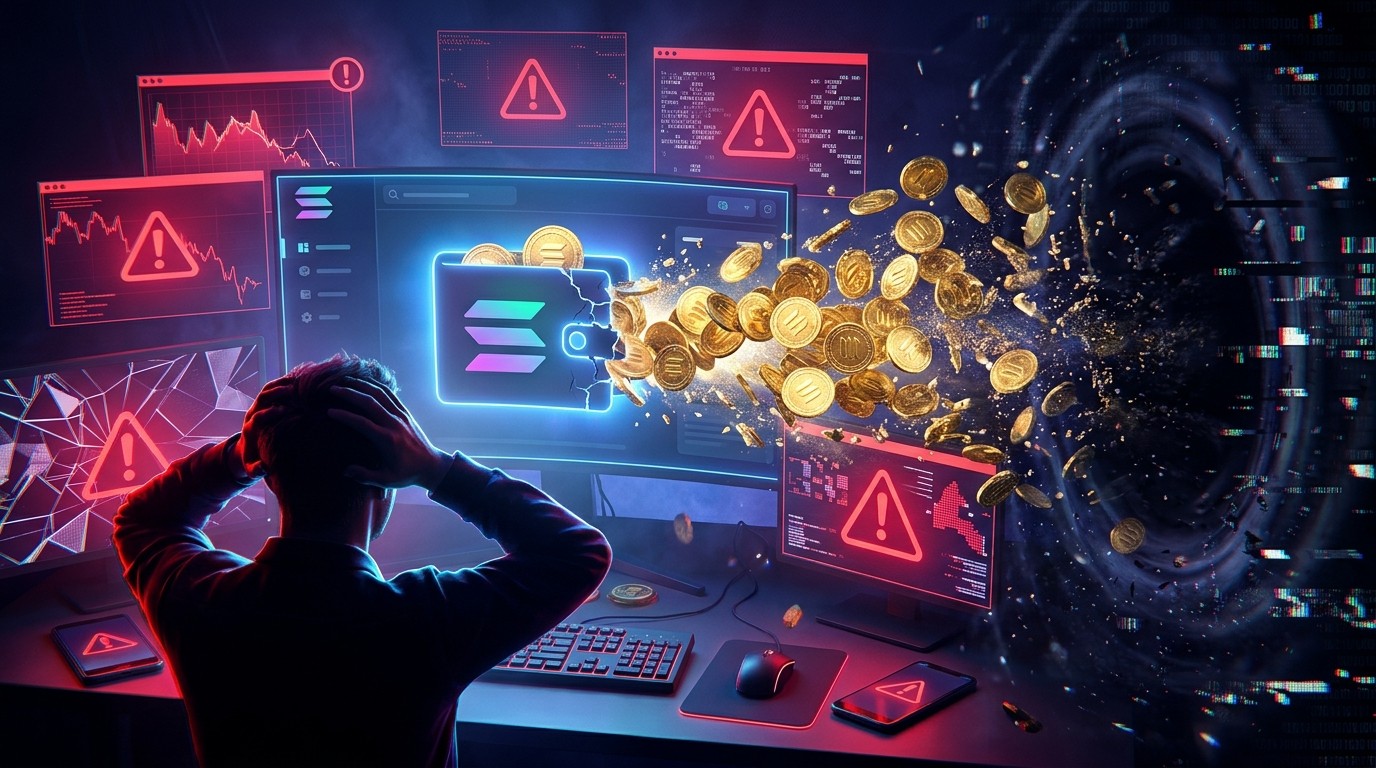

I still remember the first time I watched a Solana wallet empty itself in real time. It felt unreal, almost like watching someone pickpocket a digital vault while the owner stood right there. That same uneasy feeling returned when reports surfaced about BloomTrading users losing nearly a million dollars in SOL almost overnight. Traders woke up to empty balances, frantic messages flooded social channels, and a platform that many had trusted for automated trading suddenly found itself under intense scrutiny.
What makes this incident stand out is not only the size of the loss but the way the company responded. BloomTrading publicly promised to reimburse nine affected wallets. At the same time, blockchain trackers pointed to a much larger group of potential victims. The gap between those numbers, the unanswered questions about private keys, and the lingering uncertainty about the root cause all create a story that every Solana trader should pay attention to.
What Exactly Happened With the BloomTrading Solana Drain
In late October, multiple Solana traders began reporting unauthorized withdrawals from wallets connected to BloomTrading’s automated trading tools. The numbers were hard to ignore. Blockchain investigators estimated that roughly 9,408 SOL, valued at about $954,000 at the time, had moved into an address linked to suspicious activity. One individual reportedly lost 1,636 SOL, close to $166,000 in a single hit.
Some users said their SOL disappeared while USDC balances stayed untouched. Others described sudden transfers that left them staring at zero. A trader known in the community as Domy publicly shared that three of his wallets had been drained of around 800 SOL. He later mentioned another unexpected transfer worth roughly $64,000 and pleaded for help contacting exchanges to track the funds.
These were not isolated complaints. Multiple voices in the Solana trading community described similar experiences. The pattern suggested something systemic rather than a string of unlucky individual mistakes. Yet BloomTrading’s official response focused on nine specific wallets, creating an immediate discrepancy that still needs clear explanation.
The Company’s Public Commitment to Refunds
On October 26, BloomTrading issued a statement saying it would fully compensate the owners of nine affected wallets. The company planned to send replacement funds to new addresses provided by those users. It also pushed back against the idea of a community relief fund, insisting it would cover the losses itself.
We’re still actively investigating the root cause.
That short sentence carried weight. The firm acknowledged the possibility that a third-party service provider might have been compromised. At the same time, it stopped short of confirming any specific vulnerability, employee involvement, or external attacker. The investigation remained open, and no detailed technical report had been released at the time of the announcement.
Importantly, the pledge did not mean funds had already reached users. No payment schedule appeared. The total amount the company expected to refund stayed undisclosed. Verification methods for claims were not spelled out. In the world of crypto, promises matter less than completed transfers, and many observers are watching closely for the next update.
Why the Victim Count Matters
Blockchain monitoring accounts identified activity linked to 49 suspected victim wallets. BloomTrading spoke of nine. That difference is not trivial. It raises practical questions. Does the larger figure include wallets only loosely connected to the platform? Are some of those addresses unrelated? Or has the company simply not yet identified every affected user?
In my view, this gap is one of the most important open issues. Until the numbers are reconciled or clearly explained, trust will remain incomplete. Users who believe they were hit but fall outside the nine will understandably feel left behind. Transparency on this point would go a long way.
Private Keys and the Risks of Trading Bots
Several reports mentioned wallets whose private keys had been imported into the trading bot. That detail changes everything. A private key is the ultimate control mechanism. Whoever holds it can move the funds, full stop. Disconnecting a wallet from an application does nothing if the key itself has already been exposed.
This is not a new concern in the Solana ecosystem. Automated trading tools that require users to import keys create a concentrated risk. The convenience of hands-free trading comes with a trade-off: the service becomes a high-value target. If the platform or any connected third-party service is breached, every imported key becomes a potential liability.
I’ve always been cautious about importing private keys into any third-party tool. The convenience is real, but so is the exposure. Once a key leaves the user’s exclusive control, the security model shifts from “I control my funds” to “I trust this service to control my funds.” That trust can be expensive when it breaks.
- Never import a private key into a trading bot unless you fully accept the risk of total loss.
- Prefer tools that use session-based approvals or hardware wallet integration whenever possible.
- Move remaining assets to a brand-new wallet generated with a fresh seed phrase if you suspect exposure.
- Revoking permissions alone is not enough when the private key itself may have been compromised.
How the Drain Compared to Recent Solana Incidents
This was not the first time Solana users faced sudden unauthorized transfers. An earlier wallet exploit in September reportedly caused more than a million dollars in losses. A separate disruption at another trading platform also left users frustrated, though investigators found no direct connection to the BloomTrading situation.
What these events share is a common theme: the tension between speed and security. Solana’s fast finality and low fees make it attractive for trading bots. Those same qualities can accelerate damage when something goes wrong. Funds can leave wallets in seconds, and recovery becomes a race against time and against sophisticated movers of stolen assets.
The fact that some users reported SOL being taken while stablecoins remained suggests the attacker or the compromised process may have targeted specific assets or followed specific transaction patterns. Without a full technical post-mortem, however, that remains speculation.
What Users Should Do Right Now
If you used BloomTrading or any similar bot and imported a private key, treat the situation with urgency. Create a completely new wallet using a fresh seed phrase generated offline if possible. Transfer any remaining assets there. Do not reuse the old seed or private key under any circumstances.
Document everything. Save transaction hashes, screenshots of balances before and after, and any communications with the platform. These records matter if the company expands its refund program or if further investigation requires user evidence.
Also consider reducing reliance on any single tool that holds elevated permissions. Diversifying across wallets and limiting the amount of capital exposed to automated systems is basic risk management that many traders overlook until after a loss.
The Investigation Path Ahead
BloomTrading stated its priorities clearly: compensate affected users, determine what happened, and prevent a repeat. Those are the right priorities. Execution will decide whether the response rebuilds trust or leaves lingering doubts.
Key questions still open include the exact mechanism of the unauthorized transfers, whether a third-party provider was involved, how the company selected the nine wallets for reimbursement, and whether additional users will be covered later. A detailed technical account, once the investigation concludes, would help the broader ecosystem learn from the event.
In the meantime, the temporary pausing of some trading services suggests the company took the reports seriously enough to limit further exposure. The restoration timeline and the scope of any security upgrades remain to be seen.
Lessons for the Wider Solana Trading Community
Incidents like this force uncomfortable but necessary conversations. Automated trading tools deliver real value. They execute strategies faster than any human can and remove emotional decision-making from the process. Yet they also concentrate risk in ways that traditional self-custody does not.
Perhaps the most useful takeaway is the reminder that convenience and security often pull in opposite directions. Every time a user hands elevated control to a service, the security model changes. That change needs to be deliberate and informed rather than driven purely by the desire for better fills or lower latency.
I’ve seen too many traders treat private key imports as a minor technical step. It is not. It is a fundamental shift in who can move the funds. Treating it with the seriousness it deserves is one of the simplest ways to avoid becoming the next set of statistics.
How Refunds Fit Into Crypto Platform Accountability
When platforms step up and cover losses, it sets a positive precedent. Many services in the past have pointed to user error or terms of service and walked away. BloomTrading’s decision to reimburse at least some users is a stronger response than silence or denial.
Still, the limited scope creates its own challenges. Users outside the nine wallets may feel the response is incomplete. Clear communication about how the company identified affected parties and whether the investigation could expand the refund pool would help manage expectations.
Accountability in crypto is still evolving. There are no universal standards for how platforms should respond to security incidents. Each event becomes a case study. How BloomTrading handles the coming weeks will influence how other teams think about their own incident response plans.
Practical Steps for Safer Automated Trading
For those who still want the benefits of trading bots, several practices reduce risk without eliminating the tools entirely.
- Use dedicated wallets with limited balances for any bot interactions. Never connect your main holdings.
- Prefer solutions that support hardware wallet approvals or temporary session keys over permanent private key imports.
- Monitor connected wallets regularly rather than assuming automation means you can ignore them.
- Keep detailed records of which tools have access to which wallets.
- Have a rapid response plan ready so you can move funds quickly if something looks wrong.
These steps are not glamorous. They do not generate alpha. They do, however, keep more capital under the user’s control when things go sideways.
Looking Beyond This Single Incident
The BloomTrading situation sits inside a larger pattern of security challenges across DeFi and automated trading. As tools become more sophisticated and capital flows increase, the incentives for attackers grow. Defenders have to keep pace not only with technology but with operational discipline.
Users also carry responsibility. Choosing tools carefully, understanding the permissions granted, and limiting exposure are decisions that sit with individuals. No platform can fully protect someone who treats private keys casually.
At the same time, platforms that handle user keys or high permissions have a duty to invest heavily in security, monitoring, and transparent communication when problems arise. The combination of user caution and platform accountability is the only realistic path forward.
What to Watch in the Coming Days
Several developments will shape the next chapter of this story. First, whether BloomTrading follows through on the promised refunds and provides proof of those transfers. Second, whether the company expands the list of compensated wallets or clarifies the discrepancy with the higher on-chain estimates. Third, whether a technical post-mortem appears that explains the root cause without excessive vagueness.
Community discussion will continue. Some voices will focus on the company’s response. Others will emphasize personal security practices. Both perspectives have value. The healthiest outcome is one that improves both platform standards and individual habits.
For now, the core facts remain straightforward. A significant amount of Solana left wallets connected to a trading bot. The platform has promised to make at least some users whole. The investigation continues. And the broader lesson about private key handling is one the entire ecosystem would do well to internalize.
I’ve covered enough of these incidents to know that the details often shift as more information surfaces. What rarely changes is the underlying principle: control of private keys equals control of funds. Everything else is secondary. Keeping that principle front of mind is still the most reliable protection available.
The traders affected by this drain deserve clarity and, where appropriate, compensation. The rest of the community deserves the chance to learn from whatever findings emerge. Both outcomes depend on continued pressure for transparency and a collective refusal to treat security as an afterthought. That is the standard the space should hold itself to, whether the next incident involves a trading bot, a bridge, or something entirely new.
Until more details arrive, the prudent approach for any Solana trader remains the same. Limit exposure, question every permission, and never assume that because a tool worked yesterday it will remain safe tomorrow. In a market that moves this fast, caution is not paranoia. It is simply the price of staying in the game.