
Have you ever stopped to think about how much of our daily safety rests on machines that quietly keep things cold? I keep coming back to that thought after learning what almost happened inside several French blood storage sites. Temperatures inside the cold rooms started climbing because someone reached the refrigeration controls from the outside. The teams on site caught it quickly. Nothing was lost. Patients kept receiving what they needed. Still, the episode leaves a lingering unease that feels hard to shake.
What Actually Took Place Inside The Storage Sites
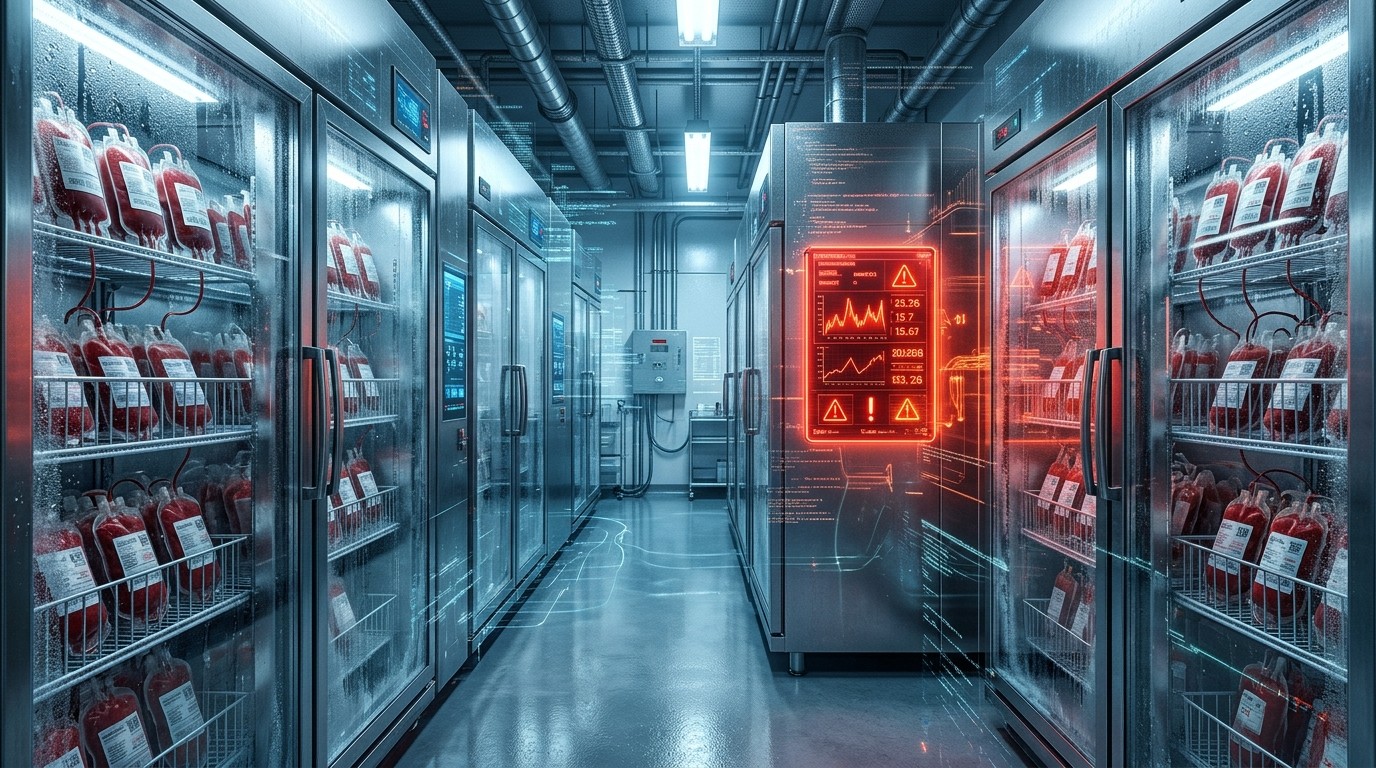
Early this week the French public blood service noticed something odd. Refrigeration equipment supplied by an outside company began behaving strangely at three different locations. The systems pushed temperatures upward in the cold storage rooms. Staff monitoring tools flagged the change almost at once. Crews stepped in, regained control of the units, and moved blood products and plasma to safer spots as a simple precaution. No samples or finished products were damaged. Service to hospitals continued without a break.
The blood service itself was not the direct target. The supplier that manages the cooling hardware took the hit. That detail matters. It shows how a weak point in one company’s network can ripple into a national medical resource. Plasma for transfusions, whole blood units, and research samples all sit inside those rooms. Any sustained temperature rise could have forced a difficult decision about whether the products remained usable.
Investigators from the national cybersecurity agency and the health ministry are now examining the event. They want to understand exactly how the remote command reached the controllers and whether the same pathway still exists elsewhere. I find it reassuring that the alarm systems worked as designed. At the same time, the fact that the intrusion succeeded at all raises questions about how many other medical cooling setups sit exposed in similar ways.
The Wider Pattern Across European Stores
The same day and the day before, supermarket chains in several countries reported almost identical problems. Freezers and display cases suddenly climbed toward temperatures that made the food unsafe. Belgium, Luxembourg, Sweden, Italy and Germany all saw stores forced to discard stock. Some independent operators under larger banners were affected while fully integrated chains also reported incidents. One large French retailer saw fifteen locations in Belgium hit in a single wave.
A month earlier a similar campaign had already swept through hundreds of French stores. Controllers that manage temperature were taken over remotely and instructed to warm up. Food waste followed. The latest events feel like a continuation rather than a fresh invention. Someone or some group has discovered that many commercial refrigeration units share the same remote management interfaces and that those interfaces are often reachable from the public internet.
Cybersecurity specialists have been clear about the basic steps. Identify every networked controller. Confirm it carries the latest security updates. If the device does not need internet access for daily work, pull it offline at once. Isolation does not cure the underlying flaw, yet it stops an attacker from issuing new commands while permanent fixes are prepared. Many independent store owners operate under cooperative brands, so their equipment and software versions can differ from the main company standard. That patchwork makes consistent protection harder.
Why Blood Storage And Food Cooling Share The Same Risk
Both systems rely on digital controllers that receive instructions about set points, defrost cycles and alarms. Those controllers often sit on networks that were never designed with hostile remote access in mind. Over the years manufacturers added convenience features that let technicians adjust settings from a distance. Convenience became exposure. Once an attacker locates an open interface, the rest can be surprisingly simple.
In the blood service case the monitoring layer still functioned. Alarms sounded. Staff reacted. The products were moved. In many supermarket cases the first sign of trouble was the temperature reading itself, sometimes after the damage had already begun. The difference in outcome underlines how critical continuous, independent monitoring remains. A secondary system that cannot be silenced by the same intrusion path can buy precious time.
I keep wondering how many other temperature-sensitive operations use the same class of equipment. Vaccine storage, pharmaceutical warehouses, laboratory reagents, even certain industrial processes all depend on stable cold. A coordinated push against those systems could create shortages or force expensive emergency transfers. The blood bank episode stayed contained. The next one might not.
Practical Steps Organizations Can Take Right Now
First, map every device that can change temperature settings. Include older units that still sit on the network because nobody has replaced them. Second, test whether those devices answer from outside the building. Simple scanning tools used by security teams can answer that question in minutes. Third, remove public internet access wherever possible and replace it with tightly controlled virtual private connections that require multi-factor authentication.
- Update firmware on every controller as soon as vendors release patches
- Segment the refrigeration network so a breach in one area cannot reach the rest
- Install independent temperature sensors that report through a separate channel
- Train staff to treat sudden temperature alarms as potential security events, not only mechanical faults
- Keep an inventory of alternative storage locations that can accept products on short notice
None of these measures is exotic. Most of them already appear in standard industrial control guidance. The difficulty lies in applying them consistently across hundreds of sites that may be owned by different operators. In my experience the organizations that succeed treat the cooling system as part of the critical infrastructure rather than a background utility. That shift in mindset changes budget priorities and maintenance schedules.
The Human Side Of A Near Miss
Behind every technical report sit people who work night shifts checking alarms and moving crates of plasma when something goes wrong. The blood service teams acted without drama. They protected the inventory and kept the supply line open. That quiet competence deserves recognition. At the same time, the knowledge that an outside party briefly held the power to ruin those products must weigh on the staff. Trust in the tools they rely on every day takes a small hit.
Patients never felt the disruption. Hospitals continued to receive the units they ordered. That outcome is the one that counts. Yet the episode still serves as a reminder that medical logistics rest on digital foundations that can be shaken from afar. When those foundations wobble, the people closest to the equipment absorb the first stress.
The monitoring and alarm systems enabled the rapid identification of these anomalies and the implementation of necessary measures to ensure that no blood samples or products were compromised.
That statement from the blood service captures the decisive factor. Detection worked. Response followed. The products stayed safe. Future success will depend on making sure the same detection layer exists everywhere temperature control matters.
Looking At The Broader Security Landscape
Attacks against operational technology have grown more frequent in recent years. Water plants, energy grids and manufacturing lines have all faced remote interference. Refrigeration systems simply join a lengthening list. The motivation can range from pure disruption to financial pressure or testing of capabilities. Whatever the reason, the effect on the ground is the same: temperature rises, product is threatened, staff scramble.
Perhaps the most interesting aspect is how ordinary the technology involved appears. These are not exotic military systems. They are commercial controllers sold to hospitals, laboratories and grocery chains. The same model that works well in a quiet warehouse becomes a liability once an attacker discovers it. Security by obscurity never lasts. Once the method is known, every similar installation becomes a candidate.
Vendors carry part of the responsibility. Devices shipped with default passwords or open remote ports create the initial opening. Operators carry the rest. Leaving those ports reachable after installation keeps the opening alive. Shared responsibility is the only realistic path forward. Neither side can solve the problem alone.
What Comes Next For Critical Cold Storage
Investigations will continue. Technical details of the intrusion path will eventually surface in confidential briefings. Public recommendations will follow. In the meantime every organization that stores temperature-sensitive material should treat this week’s events as a live drill. Ask the hard questions. Can an outsider change the set point of any unit we operate? How fast would we know? How quickly could we move the contents?
Some operators will discover they already follow good practice. Others will find gaps that need immediate attention. The cost of closing those gaps is usually far lower than the cost of a single spoiled shipment or a forced recall. Insurance policies may not cover every consequence of a cyber-induced temperature failure. Prevention remains the cheaper option.
I have watched similar stories unfold in other sectors. The pattern is familiar. A near miss occurs. Attention spikes. Budgets open. Then attention drifts and the next near miss arrives. Breaking that cycle requires treating remote access to physical systems as a permanent risk rather than a temporary scare. Continuous monitoring, regular testing and a willingness to disconnect convenience features when they create exposure form the core of a durable approach.
Lessons That Reach Beyond Blood Banks
The same principles apply to any facility that depends on precise environmental control. Data centers, clean rooms, seed banks and certain food processing plants all live or die by temperature stability. A successful intrusion against one category of controller can be adapted to another with only modest changes. Defenders need to assume that techniques proven against supermarket freezers will eventually appear against more sensitive installations.
Cross-sector information sharing helps. When one industry experiences an attack, others can examine their own equipment for the same interface or the same software version. That kind of rapid comparison shortens the window of exposure. Regulators can also play a constructive role by requiring basic security baselines for devices that control life-critical or high-value processes. Voluntary guidelines have value, yet mandatory minimums create a floor that every supplier must meet.
In the end the story returns to the people who keep the systems running. Engineers, technicians and operators who understand both the mechanical and the digital sides of the equipment form the strongest defense. Training that covers security alongside traditional maintenance skills prepares them to recognize anomalous behavior early. Empowering them to isolate a suspicious device without waiting for lengthy approval chains can stop an incident before it escalates.
A Quiet Warning Worth Hearing
Nothing dramatic happened to the blood supply this week. Temperatures rose briefly. Alarms sounded. Staff responded. Products moved. The system held. That success should not lull anyone into thinking the underlying weakness has vanished. The same remote pathway that allowed the intrusion still exists in many other places. The next attempt may arrive with less warning or against a less prepared target.
Keeping blood products safe is only one piece of a larger puzzle. Food safety, pharmaceutical integrity and laboratory research all depend on the same class of technology. Strengthening those systems benefits everyone who relies on them, which is essentially all of us. The technical fixes are known. The organizational will to apply them consistently remains the open question.
I leave the topic with a simple observation. Modern life runs on quiet machines that most of us never see. When those machines can be reached and altered from a distance, the quiet becomes fragile. This week the fragility showed itself in blood bank cold rooms and supermarket freezers. The response was effective. The lesson is clear. Protect the controllers, watch the temperatures, and never assume that convenience features come without cost.
The French blood service demonstrated that rapid detection and decisive action can neutralize a remote threat before lasting damage occurs. Other organizations that store temperature-sensitive materials now have a concrete example to study. Mapping their own exposure, closing open pathways and reinforcing independent monitoring will determine whether the next incident ends as cleanly. The tools exist. The choice to use them sits with every operator who depends on cold.
In the weeks ahead more details about the intrusion method will likely emerge through official channels. Those details should guide practical upgrades rather than fuel abstract debate. Every controller that still answers to the public internet is a potential repeat of the same story. Removing that answer, segmenting the networks and verifying that alarms cannot be silenced remotely form the practical starting point. The rest follows from sustained attention and a refusal to treat remote access as a free convenience.
Ultimately the episode underscores a broader truth about interconnected systems. A vulnerability in a supplier’s equipment becomes a vulnerability in the national blood supply. A weakness in commercial refrigeration becomes a threat to food stocks across multiple countries. The connections are real. The defenses must match that reality. Treating every temperature control device as a potential entry point changes how organizations design, maintain and monitor those devices. That change is overdue and still entirely achievable.