
Have you ever received a message that felt a little too perfect, promising easy returns on a crypto investment after a few friendly chats? I have, and the uncomfortable truth is that these approaches often hide organized networks that move faster than most people realize. When major platforms step in alongside government agencies, the scale of the problem becomes clearer. Recent coordinated action shows just how seriously the industry and authorities are taking the shift of these operations into new regions.
Coinbase Teams Up In London To Disrupt West African Scam Networks
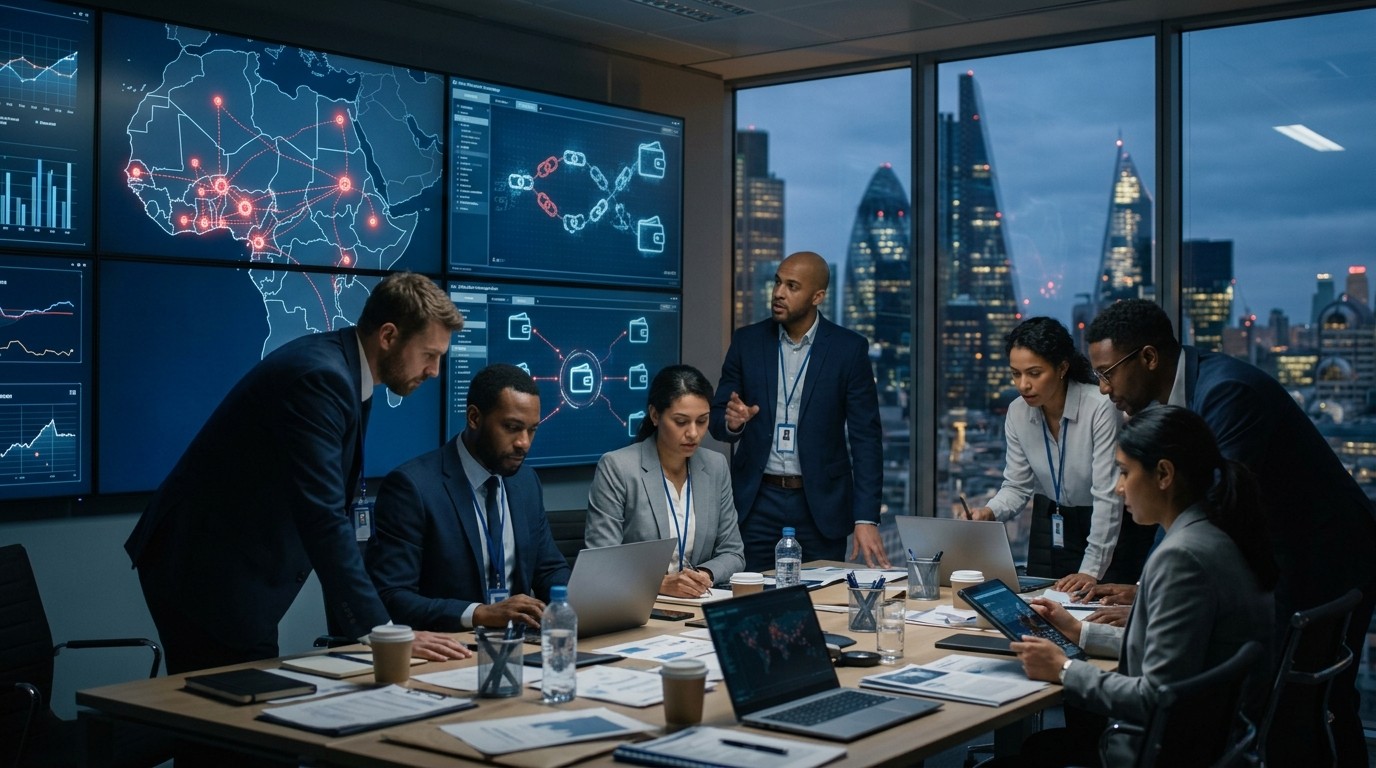
Over four intense days in early October, investigators from a leading exchange sat down with partners from the United States and the United Kingdom to target the infrastructure behind West African scam operations. The focus was not abstract. Teams traced the movement of illicit funds, supported requests to freeze related assets, and passed intelligence in real time. What stood out to me was the practical combination of blockchain analysis with everyday digital footprints such as fake profiles and messaging accounts.
The gathering, held in London, brought together technology firms, telecommunications providers, financial services, and law enforcement. African partners were also involved, and the work continues beyond those four days. In my view, this kind of sustained pressure matters more than any single announcement because criminal groups adapt quickly when one region becomes harder to operate in.
What The Joint Disruption Week Actually Involved
The operation ran from the sixth to the ninth of October. Participating teams examined accounts, digital infrastructure, and payment systems linked to networks based in West Africa. Investigators connected on-chain transfers to off-chain evidence gathered from social media and messaging platforms. That cross-referencing allowed them to spot relationships that would otherwise look random.
One practical outcome was the ability to flag and help freeze assets tied to the schemes. Real-time sharing of information meant law enforcement could act while the trails remained hot. I find this approach more effective than waiting for lengthy reports that arrive after the money has already moved several times.
Technology companies sat alongside financial institutions and police. The host role belonged to the UK agency working in partnership with the US strike force focused on scam centers. The atmosphere, from the descriptions shared, felt operational rather than ceremonial. People were there to disrupt, not just to discuss.
How Investigators Followed The Money
Blockchain leaves a public trail, yet scammers still try to obscure it. The exchange’s global intelligence specialists specialized in following those trails while linking them to other data sources. Fake investment websites, messaging accounts used to build trust, and social media profiles that looked legitimate all fed into the same picture.
By combining financial records with information held by other services, teams could identify patterns that isolated analysis would miss. Perhaps the most interesting aspect is how ordinary-looking digital activity becomes evidence once the financial layer is added. A profile that posts motivational content suddenly connects to a series of wallet movements that match known scam flows.
Support for asset freezes formed a concrete part of the work. When investigators could demonstrate clear links, the legal mechanisms already in place could move faster. This is not magic. It is methodical work that requires both technical skill and cooperation across borders.
The Specific Schemes That Were Targeted
Several familiar tactics appeared in the briefings. Fraudulent cryptocurrency investment offers ranked high. Victims are shown fabricated dashboards, early small profits, and then pressure to invest larger sums. Once the money moves, communication often changes tone or disappears entirely.
Another approach involved criminals posing as law enforcement officers. They contact people claiming an investigation is underway and demand payment to clear a supposed problem. The pressure is intense because the caller already seems to know personal details, often gathered earlier through social engineering.
Staged video-call arrests added a new layer of urgency. Victims are shown what looks like an official proceeding and told that sending funds will resolve the situation. The combination of visual evidence and time pressure makes rational decision-making harder. I have seen similar tactics described in other contexts, and the emotional impact is real.
Social media serves as the initial hunting ground. Messaging apps become the relationship-building stage. Financial services, including crypto platforms, become the final transfer point. Breaking any one of those links helps, but the coordinated effort aimed at all of them simultaneously.
Why The Focus Shifted Toward West Africa
Earlier in the year, similar coordinated action targeted compounds operating in Southeast Asia. That pressure appears to have pushed some networks to expand or relocate activity toward West Africa. Criminal groups do not stay static. When one operating environment becomes riskier, they look for alternatives.
A senior leader at the exchange noted that the earlier disruption proved coordinated industry and law-enforcement work can deliver results. The current effort is framed as continued pressure rather than a one-off event. That framing feels realistic to me. These networks rebuild quickly unless the pressure remains consistent.
The presence of African law-enforcement partners in the London discussions signals recognition that local knowledge matters. International cooperation works best when it includes the regions most directly affected by the operations themselves.
The Wider Agreement Between US And UK Authorities
Before the London week, American and British authorities formalized an arrangement covering joint investigations into cryptocurrency investment fraud and related online schemes. The agreement allows information exchange about organized groups, identification of common targets, and decisions about which jurisdiction should lead prosecution when cases overlap.
Several shared cases of interest had already been identified. The October disruption event with private-sector partners was planned as a practical next step. Having clear rules of engagement between the two countries reduces the friction that often slows cross-border cases.
For victims in the United States, reported losses from online investment fraud reached striking levels. Figures cited for 2025 showed 8.65 billion dollars, a sharp rise from the previous period. Officials noted that actual totals are likely higher because many people never report. That under-reporting is a persistent challenge in this space.
The strike force’s mandate covers cryptocurrency investment fraud, related human trafficking, and the money-laundering networks that support scam centers. The breadth of the remit reflects the reality that these operations rarely stay within a single crime type.
Lessons From Earlier Disruptions
In a previous operation, the same exchange reported freezing more than three million dollars in cryptocurrency tied to Southeast Asian networks. Intelligence was shared with multiple agencies and technology partners. Parallel actions by social platforms disabled large numbers of accounts and pages. A major software company suspended thousands of fraudulent accounts. Satellite connectivity providers terminated thousands of kits linked to unlawful use.
Those numbers illustrate the multi-layered approach. Freezing funds matters. Removing the digital storefronts and communication channels matters just as much. When several points of leverage are applied together, the operational cost for the networks rises.
Later actions targeted vendors who supplied services to the compounds. One marketplace and its associated vendors faced restraints totaling tens of millions in cryptocurrency. Wallets were seized and additional restraints sought. Channels used to advertise laundering and recruitment services were also taken offline through court authorization.
The pattern is consistent. Follow the money, remove the tools, and raise the risk of detection. Each successful operation adds to the collective understanding of how these networks function.
The Scale Of Suspicious Activity Flagged By Financial Authorities
Separate analysis from the US financial intelligence unit examined tens of thousands of reports filed by financial institutions. The total suspicious activity linked to digital-asset investment scams reached 12.7 billion dollars across a multi-year window. Victims appeared in every state and several territories.
Money services businesses, many of them digital-asset firms, filed a substantial share of the reports and identified billions in suspicious flows. Traditional banks reported another large portion. The numbers are not pure loss figures. They include attempted transfers, possible reporting overlaps, and other caveats. Still, the volume is hard to ignore.
Blockchain analysis within that review showed a common pattern. Proceeds were typically converted into stablecoins, predominantly one major dollar-pegged token, before moving through decentralized services or exchanges located outside the United States. That conversion step is a recurring feature in many investigations.
Some victims financed their transfers through retirement accounts, home equity, second mortgages, or personal loans. The personal cost extends far beyond the immediate financial loss. I have spoken with people who describe the aftermath as a combination of financial recovery and emotional rebuilding that can take years.
How These Scams Often Begin In Everyday Digital Life
Many approaches start on social platforms where profiles appear friendly and successful. A connection request or a comment under a post can open the door. Conversation moves to private messaging. Over days or weeks, trust is built. Stories of profitable crypto trades appear. Screenshots of growing balances are shared. The invitation to participate follows.
The investment platform the victim is directed to looks professional. Early small withdrawals sometimes succeed, reinforcing confidence. Then larger amounts are requested, often with time pressure or claims of limited opportunity. Once the funds leave the victim’s control, recovery becomes difficult.
Police impersonation and staged video arrests add another vector. These do not always begin with investment talk. They can start with a claim that the person’s identity has been used in a crime or that an account is under investigation. The demand for payment to resolve the issue creates urgency that overrides caution.
In both cases, the emotional levers are similar. Trust, fear, and the desire for a quick resolution. Understanding those levers helps people pause before acting. That pause is often the difference between a close call and a significant loss.
Practical Steps Individuals Can Take
Verification remains the strongest defense. Any unsolicited investment opportunity deserves independent checking. Official channels exist for confirming whether someone claiming to be law enforcement is genuine. Video calls that demand immediate payment should trigger skepticism rather than compliance.
- Treat unexpected contact about investments or legal problems with caution
- Never send funds based solely on screenshots or video claims
- Use official websites and apps rather than links provided in messages
- Enable strong authentication on all financial and messaging accounts
- Discuss large or unusual transfers with a trusted person before acting
These steps sound basic, yet they address the exact pressure points the schemes rely on. Scammers count on isolation and urgency. Introducing a second opinion or a short delay often breaks the script.
Platforms themselves continue improving detection of suspicious patterns. Users who report unusual activity contribute to the larger picture that investigators later use. The feedback loop between individual reports and systemic response is more important than many people realize.
Why Industry Participation Changes The Equation
Exchanges and other financial services sit at a unique vantage point. They see transaction patterns that pure law-enforcement analysis might reach more slowly. When those firms actively share intelligence under appropriate legal frameworks, the speed of response increases.
The London week demonstrated that private-sector investigators can work alongside government teams without compromising either side’s role. The exchange’s team focused on tracing and intelligence sharing. Law enforcement retained the authority to seek freezes and pursue prosecutions. That division of labor feels both practical and necessary.
Technology and telecommunications partners brought their own data and disruption capabilities. Removing accounts, terminating connectivity, and shutting down fraudulent sites all raise the cost of running the networks. No single actor can do everything. The combination produces results that isolated efforts cannot.
Looking Ahead At Continued Pressure
The work described as ongoing after the four-day event is the part that will determine longer-term impact. Networks that lose infrastructure in one location will attempt to rebuild elsewhere. Sustained attention across regions is required to keep the operational costs high.
Agreements between major jurisdictions provide a foundation for that continuity. Shared case lists and clear rules for deciding prosecution venues reduce the chance that important targets fall between institutional gaps. Private-sector partners who have already demonstrated willingness to engage are likely to remain involved.
For ordinary users of digital assets, the message is mixed but ultimately constructive. The existence of sophisticated scam networks is real and evolving. At the same time, the response capacity of both industry and government is also evolving. Each successful disruption adds tools and knowledge that can be applied to the next set of cases.
I remain cautiously optimistic. The shift of activity toward West Africa shows adaptation by the networks. The rapid organization of a multi-party response in London shows adaptation on the other side as well. That contest will continue. Staying informed and maintaining healthy skepticism remain the most reliable personal defenses.
The Human Cost That Numbers Alone Cannot Capture
Behind every large figure are individual stories. People who liquidated savings, borrowed against homes, or emptied retirement accounts because a carefully constructed narrative convinced them the opportunity was genuine. The recovery process involves both financial and psychological dimensions. Trust in digital interactions can take a long time to rebuild.
Support resources exist, yet many victims feel embarrassment that delays them from seeking help. Reducing that stigma is part of the broader public conversation that needs to continue. Reporting the experience, even when the funds appear gone, still contributes data that helps identify patterns and protect others.
Law-enforcement and industry efforts ultimately aim at reducing the number of people who become victims in the first place. Freezing assets and disrupting infrastructure are means to that end. The more effectively those tools are applied, the fewer households face the aftermath.
Building Better Personal Defenses Over Time
Education remains uneven. Some users of digital assets are highly sophisticated about on-chain risks yet still vulnerable to social engineering. Others understand social risks but underestimate how quickly funds can move once they leave a regulated platform. Bridging those knowledge gaps takes repeated, practical communication rather than one-time warnings.
Families and friend groups that talk openly about these tactics create informal early-warning systems. A quick message asking “does this sound right to you?” can interrupt the isolation that scammers prefer. Community-level awareness complements the institutional efforts described in the London operation.
Platforms continue refining their detection models. Users who keep software updated, enable available security features, and treat unexpected financial requests with caution form the first line of defense. Institutional action provides the second and third lines. Both are necessary.
Why Coordinated Action Matters More Than Ever
The speed at which these networks can reconstitute themselves after a disruption is high. A single successful operation that freezes funds and removes accounts buys time, but without follow-through the advantage erodes. The decision to treat the London week as part of ongoing pressure rather than a standalone event reflects that understanding.
Cross-border information sharing reduces the safe harbors that organized groups once enjoyed. When investigators in one country can rapidly pass leads to counterparts in another, the window for moving assets narrows. Private-sector data adds volume and speed that government systems alone sometimes lack.
In my experience covering these developments, the most effective periods of disruption have always combined technical tracing, legal authority, and industry cooperation. Missing any one of those elements leaves gaps that determined networks will exploit. The recent London gathering brought all three into the same room for four focused days. That combination is worth noting.
The expansion into West Africa demonstrates that pressure in one region produces displacement rather than permanent elimination. Future operations will likely need to anticipate the next geographic or technological shift. Maintaining the partnerships that made the October effort possible will be essential for keeping pace.
Final Thoughts On Staying Alert
Digital assets offer genuine utility and opportunity. They also attract sophisticated criminal attention. The balance between those two realities is managed through a combination of personal vigilance and institutional response. The joint work in London is a concrete example of the latter. Individual caution remains the foundation of the former.
When an offer appears too convenient, when urgency is manufactured, or when official-sounding claims arrive through unofficial channels, the safest default is to slow down and verify. That habit, repeated across millions of users, raises the overall cost of running scam operations. Paired with the kind of coordinated disruption described here, it forms a practical defense that continues to evolve.
The networks will keep adapting. So will the people and institutions working to contain them. Staying informed about both sides of that contest is one of the more useful investments anyone can make in this space.