
I still remember the first time I unboxed a hardware wallet. The packaging felt solid, the device looked clean, and that little sense of security was almost physical. You assume the product that arrives at your door is exactly as the manufacturer intended. Recent events show that assumption can be dangerous. On October 15, 2026, Ledger announced major changes to how its authorized retailers sell and store devices after criminals managed to slip hidden electronic components into genuine wallets. Those implants captured recovery phrases during setup and sent the data out over cellular networks. The result was a coordinated theft that independent investigators estimate exceeded $86 million.
How Hidden Implants Turned Trusted Devices Into Traps
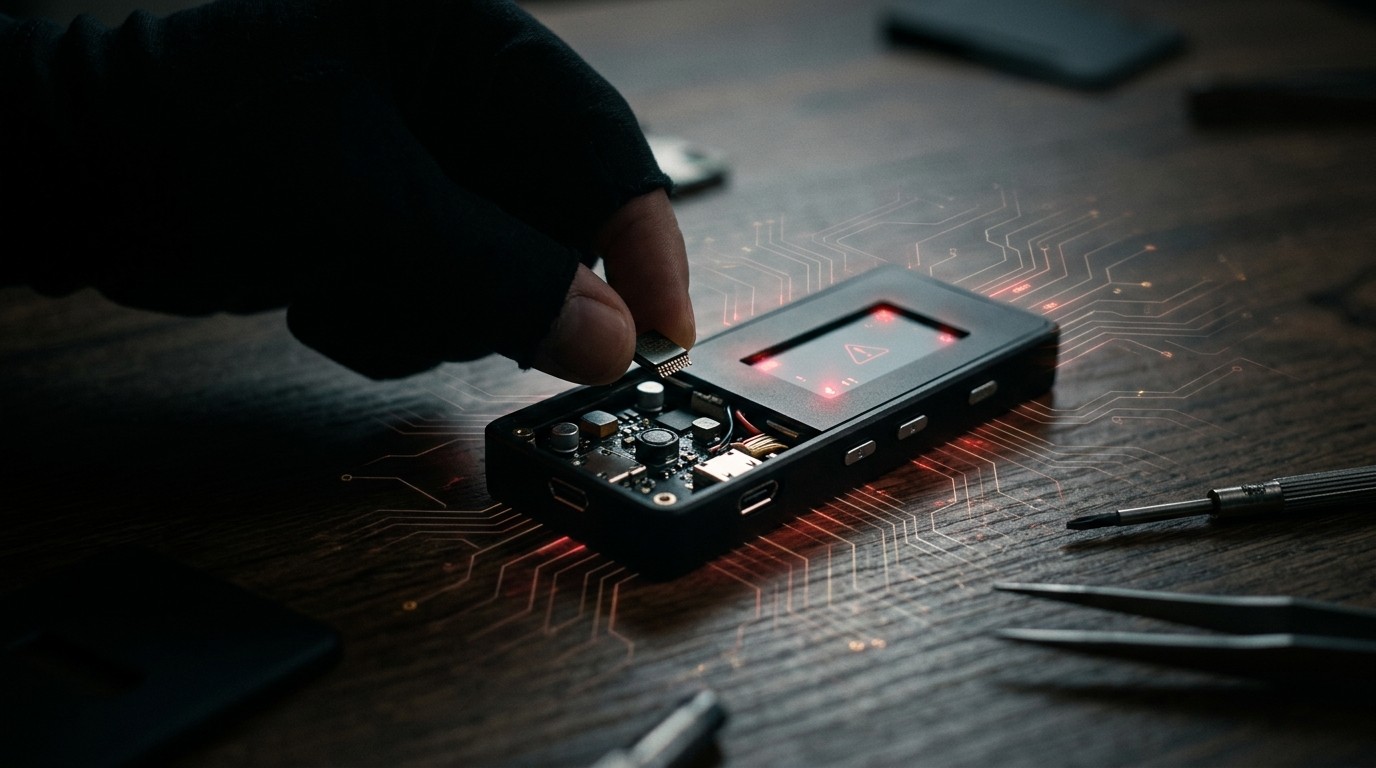
The attackers did not hack Ledger’s factories or breach its secure chips. They bought legitimate devices, carefully opened them, and inserted custom electronics designed to read the recovery phrase as it appeared on the screen. Then they put the wallets back into circulation through distribution channels, mainly in Southeast Asia. It was patient, expensive, and methodical work. Ledger’s own security team later said the group had spent millions preparing the operation.
A recovery phrase is usually 24 words. Anyone who obtains those words can recreate the wallet on another device and move the funds. The implant waited for the exact moment the phrase appeared, captured the text with a small microcontroller, and transmitted it through an embedded SIM card using an LTE connection. Crucially, the malicious component operated independently of the device’s Secure Element. It never needed to alter the operating system or change transaction signatures. That made the attack quieter and harder to spot during normal use.
The implant operated independently of the device’s Secure Element, which protects sensitive cryptographic information. Investigators found no evidence that the malicious component modified the operating system or altered transaction signatures.
In my view, this is one of the more unsettling aspects of the whole episode. The wallet still behaved normally. Transactions signed correctly. The device looked and felt genuine. Only the recovery phrase was compromised at the moment of creation. Once that information left the device, the attacker held the keys to the kingdom.
Timeline of the Discovery and Immediate Response
Reports of losses began to surface after a coordinated theft operation on October 9. By October 13, Ledger’s Donjon security team had released a technical update describing the implant. Two days later the company issued a broader statement and announced sweeping changes for its authorized retailers. Sales through resellers across Indonesia, Singapore, Thailand, the Philippines, Vietnam, Malaysia, and Hong Kong were suspended while investigators examined the channels.
One Southeast Asian reseller that had already been linked to confirmed cases stopped selling hardware wallets after customers reported losses. In Germany, a major electronics chain paused both physical and online sales of Ledger devices after a single reported implant, even though no funds were confirmed stolen in that specific case. Ledger purchased devices from stores in multiple markets, including Germany, and opened them for physical examination. Samples from warehouses and portions of the company’s own inventory were also inspected. No unauthorized components turned up in the checked units. Still, the company has not disclosed exactly how many devices were examined, so the full scale of the problem remains unclear.
Ledger described the incident as a localized distribution attack and stressed that its manufacturing systems were not responsible. Investigators are still trying to determine precisely where every affected device was modified and how the altered wallets re-entered the supply chain.
New Rules Every Authorized Retailer Must Follow
The most visible change is in how devices are handled in stores. Authorized retailers can no longer leave Ledger wallets on display shelves or counters. Products must stay in storage areas and be handed to the customer only at the moment of purchase. The goal is simple: reduce opportunities for unauthorized handling between the warehouse and the buyer.
Returned devices are now strictly off-limits for resale, even if the packaging looks unopened and the product appears unused. This rule already existed, but Ledger has instructed distributors to enforce it without exceptions. Retailers must also notify the manufacturer immediately whenever a customer reports anything unusual about a device or packaging.
- Devices stay in secure storage until the moment of sale
- No display of sealed wallets on open shelves
- Returned products cannot be sold again under any circumstances
- Immediate reporting of suspicious hardware or customer complaints
- Heightened oversight of the entire authorized distribution network
These measures feel practical rather than dramatic. They address the reality that physical access to a device before it reaches the end user creates risk. I’ve always preferred buying hardware wallets directly from the manufacturer when possible. After this episode, that preference feels less like personal caution and more like common sense.
What Users Should Do Right Now
If you bought a Ledger device through certain Southeast Asian resellers, the company has already advised against initializing it until you contact official support. For anyone who has already set up a wallet that might have been affected, the advice is clear: move the funds to a new device with a freshly generated recovery phrase. Restoring the old phrase on a replacement wallet will not help if the words were already captured.
Never share your recovery phrase with anyone claiming to represent customer support. Ledger employees will not request those words through messages, phone calls, or websites. That warning has been standard for years, yet social engineering attempts spike after every high-profile incident. A little extra skepticism goes a long way.
Perhaps the most practical habit is to treat the recovery phrase generation moment as highly sensitive. Write the words down offline, keep them offline, and never photograph or type them into any digital device. The implant in this case relied on the phrase appearing on the screen. Reducing exposure at that exact stage remains one of the strongest defenses available to individual users.
Broader Implications for Hardware Wallet Security
This attack did not break the cryptographic design of the wallet. It exploited the physical journey the device takes before it reaches a trusted owner. That distinction matters. Secure Element chips, verified firmware, and proper transaction signing all still worked. The weak link was human access during distribution.
Ledger has said it is developing additional product-level protections to make physical tampering harder. Specific technical details and timelines have not been released. The company also plans to share findings with other hardware wallet makers so the wider industry can examine similar risks. That kind of information sharing is useful. Physical supply-chain attacks are not limited to one brand.
In my experience covering security incidents, the most effective long-term responses combine better processes with better product design. Retailer rules help in the short term. Making devices more resistant to undetectable modification helps over years. Both are needed.
Why the Attack Succeeded for a Time
Several factors worked in the attackers’ favor. First, the devices were genuine. Buyers who checked packaging and serial numbers had little reason for suspicion. Second, the implant did not interfere with normal operation. Users could complete setup and make transactions without noticing anything unusual. Third, the recovery phrase was captured at the precise moment it was most vulnerable—when it was displayed for the owner to write down.
The use of cellular transmission rather than nearby radio or optical methods added another layer of stealth. Once the phrase left the device, the attacker no longer needed physical proximity. That design choice turned a local compromise into a remote one.
Independent blockchain analysts have estimated losses above $86 million. Ledger has not confirmed the exact figure or the number of affected customers. The company is working with law enforcement and industry partners to trace funds and identify the infrastructure used to collect credentials. No arrests or recovered amounts have been publicly announced yet.
Practical Lessons for Anyone Holding Crypto
Hardware wallets remain one of the stronger options for long-term storage of significant amounts. This incident does not change that fundamental point. What it does change is the level of care required around the purchase and setup process.
- Prefer purchasing directly from the manufacturer whenever possible.
- Inspect packaging carefully and avoid devices that show signs of prior opening.
- Generate the recovery phrase in a private setting and store it offline only.
- Never reuse a recovery phrase that might have been exposed.
- Move funds promptly if any doubt arises about a device’s history.
These steps are not complicated, yet they address the specific failure mode that occurred here. Physical integrity of the device before first use is now as important as the cryptographic strength of the chip inside it.
I’ve noticed that many people focus almost exclusively on software and online threats. Phishing, malware, and exchange hacks dominate conversation. Physical supply-chain risks receive less attention until something like this happens. That imbalance is worth correcting.
What Ledger Still Needs to Clarify
Several questions remain open. How many devices were actually modified? Where exactly in the distribution chain did the modifications occur? How long had the operation been running before detection? Ledger has promised further technical details once investigators can safely release them. Transparency on those points will matter for restoring full confidence.
The company has conducted what it calls its largest internal investigation, involving multiple departments and external partners. Specialists dismantled recovered implants and analyzed their operation. That work continues. Until more findings appear, the public picture is incomplete but already sufficient to justify the retail changes.
Looking Ahead for Hardware Wallet Buyers
The new reseller rules are a direct response to a real and demonstrated risk. Keeping devices out of open display and prohibiting the resale of returns reduces the window of opportunity for similar attacks. Additional product-level protections, when they arrive, should make undetectable modification harder still.
For individual users the practical takeaway is straightforward. Treat the device as untrusted until it is in your hands and you have verified its integrity to the best of your ability. Generate recovery phrases carefully. Store them offline. And if anything about a purchase feels off, contact the manufacturer before initializing the wallet.
Security in crypto is rarely about a single perfect solution. It is about reducing the number of ways things can go wrong. This episode removed one assumption—that a sealed, genuine-looking hardware wallet is automatically safe—and replaced it with a more realistic set of practices. That shift, uncomfortable as it is, ultimately strengthens the ecosystem for everyone who takes it seriously.
The investigation is ongoing. More technical information is expected. In the meantime, the combination of suspended regional sales, stricter retailer requirements, and clear user guidance forms a coherent first response. How the industry builds on these lessons will determine whether similar attacks become rarer or simply more sophisticated. For now, awareness and careful handling remain the strongest tools available to ordinary users.