
Have you ever walked into a meeting room and wondered whether someone might be listening without your knowledge? Most of us brush that thought aside. At one of the world’s most closely watched technology companies, that uneasy feeling turned out to be completely justified.
A sophisticated recording device was found tucked into the back of a television in an executive conference room. It had been carefully concealed. The discovery set off a rapid internal investigation that eventually involved federal authorities. Within days an employee was identified, terminated, and arrested. The whole episode offers a stark look at how even the most advanced organizations still face very human risks from the inside.
What Exactly Happened Inside the Office
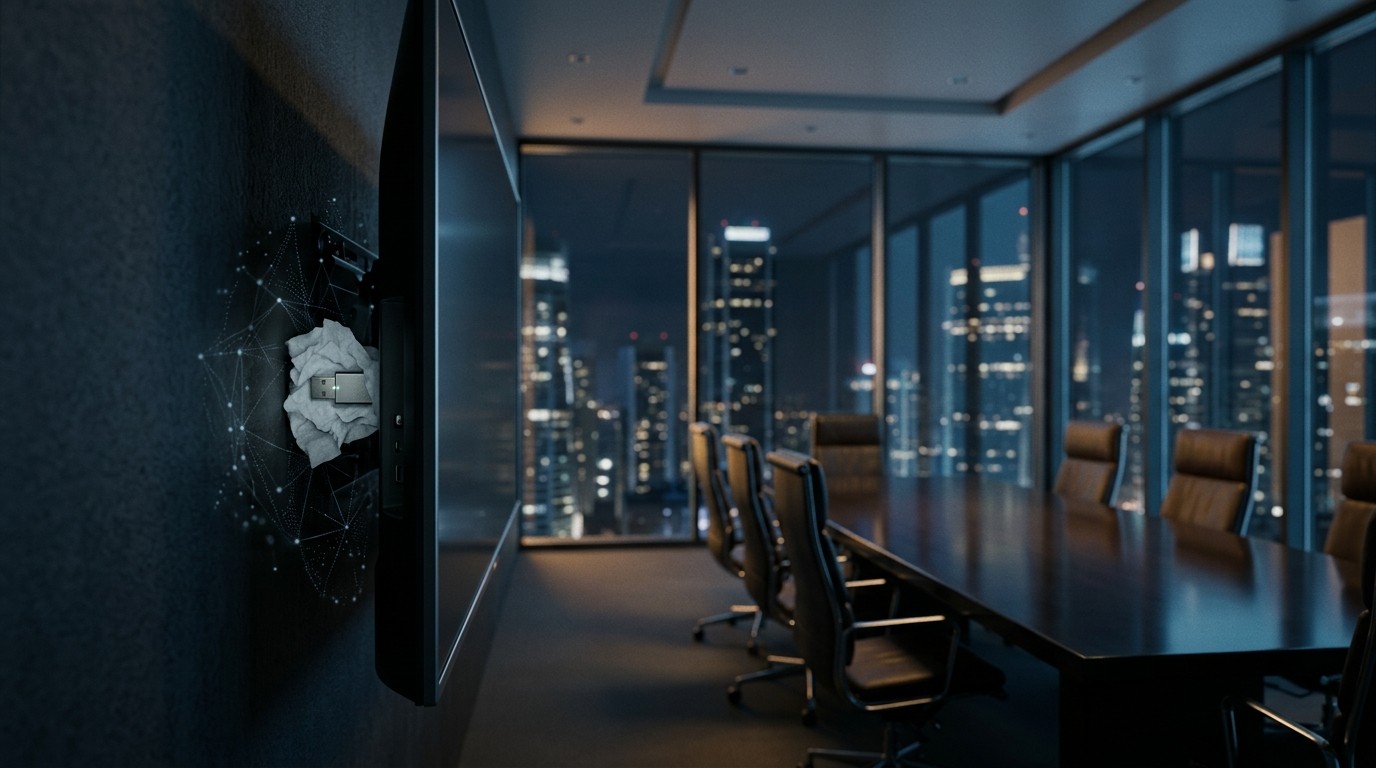
Staff first noticed something odd on or about September 30. Behind a television mounted in an executive conference room sat a small audio recording device. It had been inserted into a USB port and wrapped in ordinary toilet paper to help hide it from casual view. The device was not a cheap gadget bought online. Investigators described it as sophisticated, and its stored contents were encrypted.
Company personnel quickly determined that the device had been installed only a couple of days earlier, around September 28. That short window mattered. It meant the recording period was limited, yet the intent was clear. Someone with legitimate access to the building had deliberately placed equipment designed to capture private conversations among senior leaders.
I have covered technology and security stories for years, and this detail still stands out. Toilet paper as camouflage feels almost mundane, yet it worked well enough to delay discovery. The person who planted it clearly understood both the physical layout of the room and the daily routines that would keep the device unnoticed for a short time.
How the Company Identified the Culprit
Here is where the story takes an unusual turn. The company stated that it used its own artificial intelligence models to examine the device and trace its origin. Those models helped pinpoint a specific employee who had planted the recorder just days before. Once that identification was made, the firm moved quickly. The employee was fired and the entire matter was referred to federal investigators.
Whether conventional methods such as badge access logs or security camera footage played supporting roles remains unclear from public statements. The company has emphasized the contribution of its AI tools. That claim is interesting on several levels. It suggests the same technology the firm develops for commercial use can also serve as a defensive instrument against insider threats.
We discovered a sophisticated recording device that was hidden inside one of our offices. We used our models to understand the device and where it had come from, identifying that a specific employee had planted it a few days earlier.
The employee in question was a 35-year-old Saudi national who had joined the product team in July of the previous year. He had worked at the company for only a few months before the device appeared. Federal authorities arrested him on October 9. He remains in custody while the investigation continues.
What the Company Says Was Not Compromised
One of the most important reassurances offered publicly is that there are currently no indications the employee accessed or removed model weights, source code, or customer data. That distinction matters. Planting a recording device in a conference room is serious, yet it is different from successfully extracting the core intellectual property that powers advanced AI systems.
Still, the absence of evidence is not the same as absolute proof that nothing else occurred. Investigations of this nature often expand as digital forensics continue. The company has stated it will keep cooperating fully with federal agents. That ongoing cooperation is wise. Insider cases rarely stay neatly confined to a single device.
In my view, the real test will come in the weeks ahead as more details emerge about how the device was obtained, whether any recordings were successfully retrieved, and whether the individual acted alone or with outside direction. Those answers will shape how the broader technology community assesses the risk.
Why This Incident Feels Especially Significant
Protecting advanced AI technology has become a matter of national importance. That phrase appears in official statements for good reason. The models under development represent strategic assets. Governments around the world understand their potential value, and so do competitors. When an insider places a recording device in a senior meeting space, the concern immediately rises above ordinary workplace misconduct.
Federal officials have described the protection of American AI innovation as one of their highest counterintelligence priorities. That framing places this case in a larger context. It is no longer simply a human-resources problem. It sits at the intersection of corporate security, national security, and the rapid commercialization of powerful technology.
Consider the timing. The device was discovered in late September. The arrest followed in early October. The public disclosure came shortly afterward. The speed of the response suggests the company already had robust processes for handling potential insider threats. Many organizations would still be debating internal next steps weeks later.
The Broader Climate of Internal Tension
This episode did not occur in isolation. In the weeks leading up to the discovery, the company had already terminated several researchers over allegations involving the handling of sensitive information. Those individuals disputed the characterizations and raised concerns about the impact on internal culture. No public evidence currently links those earlier terminations to the recording device. Yet the sequence of events creates an atmosphere of heightened scrutiny.
Companies working on frontier AI systems face a difficult balance. They need open collaboration among researchers to make progress. At the same time they must protect information that, if leaked or stolen, could have significant commercial and strategic consequences. Finding that balance is harder than most outsiders appreciate.
I have spoken with security professionals at other technology firms who describe similar pressures. The more valuable the research becomes, the greater the incentive for outsiders to recruit insiders. Physical devices remain attractive because they can capture conversations that never appear in email or chat logs. A well-placed recorder in a conference room can yield insights no digital intrusion would easily obtain.
Lessons Emerging From the Response
Several practical takeaways stand out. First, physical security still matters enormously even in highly digital organizations. Badge access, camera coverage, and routine sweeps of meeting rooms remain essential. Second, the ability to analyze physical evidence with advanced models can accelerate investigations. Third, rapid escalation to law enforcement when criminal activity is suspected is often the correct path.
- Physical concealment methods can be surprisingly low-tech yet effective
- Short installation windows still pose real risk if the location is high-value
- Encrypted storage on the device complicates immediate content recovery
- Employee tenure of only a few months does not eliminate insider risk
- Public transparency after the fact can help rebuild confidence
Perhaps the most interesting aspect is the company’s willingness to credit its own models for helping identify the individual responsible. That claim invites both admiration and careful scrutiny. Outside confirmation of exactly how the models contributed has not been provided. Independent verification would strengthen the narrative. Until then, the statement stands as an assertion from the organization that experienced the breach.
What Remains Unknown
Important questions linger. How long was the device actively recording before discovery? Were any of its encrypted contents successfully recovered and reviewed? Did the individual act independently or with external guidance? Were additional devices or digital access attempts ever identified? Answers to these questions will determine whether this incident is viewed as a contained failure or the visible tip of a larger problem.
Federal investigators have characterized the case as ongoing. That language is standard, yet it also signals that more information may surface. Companies in similar positions often learn additional details only after forensic work and interviews progress further. Patience is required, even when the initial public narrative already feels dramatic.
In the meantime, other organizations developing sensitive technology would be wise to review their own physical security postures. Conference rooms used by senior leadership deserve particular attention. Simple measures such as periodic physical inspections, restrictions on personal devices in certain spaces, and clear reporting channels for suspicious findings can reduce risk.
The Human Element Behind Technical Defenses
Technology can detect anomalies and accelerate analysis. Ultimately, however, people decide to plant devices or to report them. Culture plays a larger role than many security frameworks acknowledge. When employees feel that raising concerns will be met with seriousness rather than suspicion, early detection becomes more likely.
The individual who installed the recorder had been with the company only a short time. That fact underscores a recurring challenge. Background checks and onboarding processes can never eliminate all risk. Continuous monitoring of access patterns, combined with a culture that encourages vigilance, offers stronger protection than any single technical control.
I find myself returning to the image of a small device wrapped in toilet paper behind a television. It is almost ordinary in its presentation. Yet the potential consequences of the conversations it might have captured are anything but ordinary. That contrast captures the modern security dilemma perfectly. Threats can arrive dressed in the most unremarkable packaging.
Looking Ahead at Corporate and National Stakes
The protection of advanced AI systems will remain a high priority for both private companies and government agencies. Incidents like this one serve as reminders that the perimeter is not only digital. Physical spaces where decisions are discussed and strategies are shaped require equal attention.
Companies will continue refining both their technical detection capabilities and their human processes. Law enforcement will continue treating certain categories of insider activity as matters of national interest. The rest of us will watch to see how transparent the eventual outcomes become.
For now, the public facts are relatively straightforward. A sophisticated recording device appeared in a sensitive location. The company used available tools to identify the employee responsible. Federal authorities made an arrest. No evidence of major data exfiltration has been disclosed. The investigation continues.
Those facts alone are enough to hold attention. They also raise deeper questions about trust, access, and the growing strategic value of the technology at the center of the story. How organizations answer those questions in the months ahead will matter far beyond any single conference room.
The device itself may already be in evidence lockers. The conversations it recorded, if any were recovered, will be reviewed by professionals trained for such work. The employee faces the legal process. The company returns to its daily work of building systems that many believe will reshape entire industries. And the rest of the technology world takes quiet notes on what can go wrong even inside the most carefully guarded offices.
Security is never finished. It is a continuous practice of anticipation, detection, and response. This episode illustrates both the progress that has been made and the persistent vulnerability that remains whenever human beings with legitimate access decide to cross a line. That vulnerability is unlikely to disappear. The best organizations simply get better at finding it quickly when it appears.
In the end, the story is less about one device and one arrest than about the environment in which such events can still occur. As the capabilities of AI systems expand, the incentives to obtain information about them will only grow. Physical and digital defenses will need to keep pace. The recent discovery shows that at least one major player is treating the problem with the seriousness it deserves. Whether that seriousness becomes industry standard remains an open and important question.
Readers who work in technology or security roles may already be reviewing their own meeting rooms with fresh eyes. That reaction is healthy. A little constructive paranoia, paired with practical controls, often proves more effective than any single advanced tool. The ordinary toilet paper wrapping around an extraordinary device is a useful reminder that threats rarely announce themselves with dramatic flair. They simply wait, quietly, for the right moment to listen.