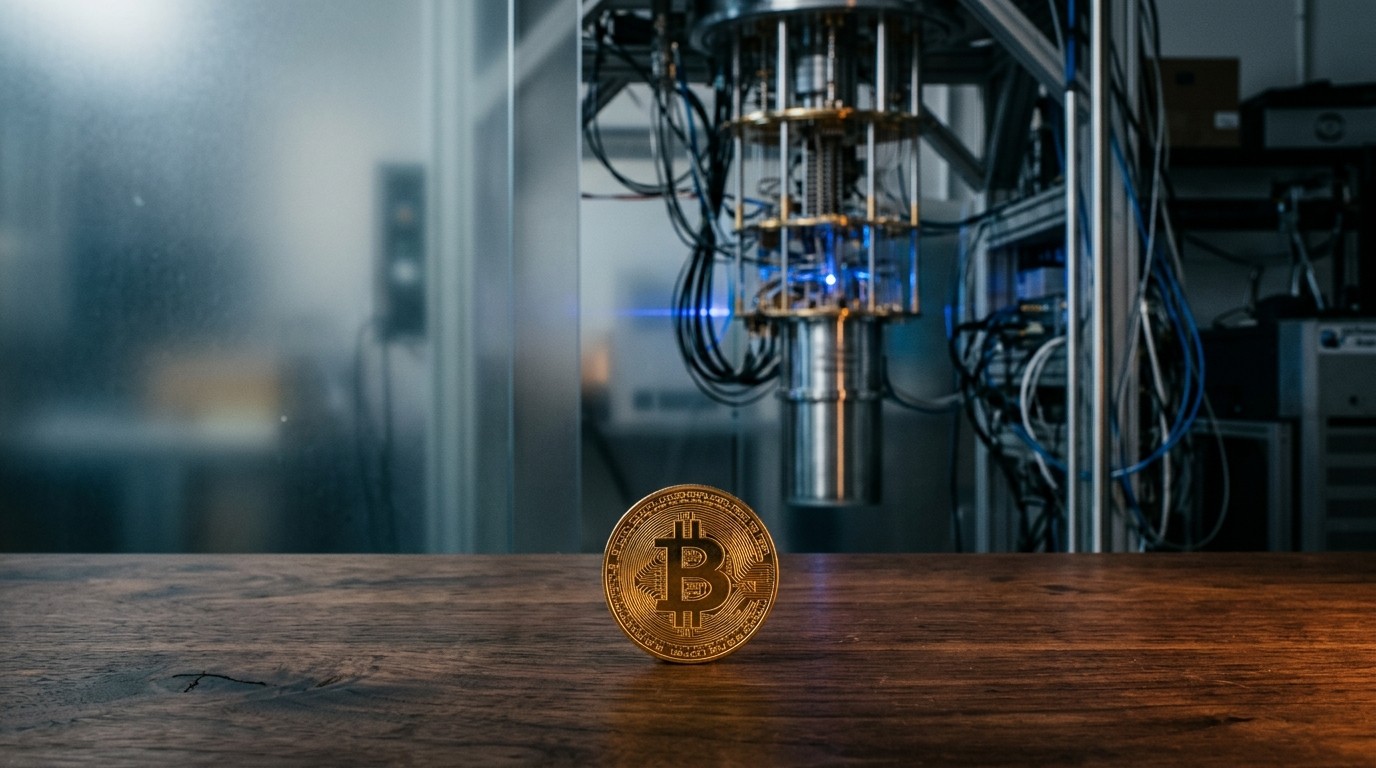

That gap, between the story and the hardware, is the whole argument. Fear has a schedule. Engineering rarely does. If you hold Bitcoin, or you are only trying to decide whether the scare is worth losing sleep over, the useful question is not whether quantum physics is real. It is. The useful question is whether a cryptographically relevant quantum computer is close enough to change how you store coins this year, or even this decade. I do not think it is. Not on the evidence we have.
The Scare Is Older Than The Machine
Bitcoin has collected doomsday stories the way a harbor collects barnacles. Each cycle brings a fresh reason the whole thing is supposed to fail. Sometimes the story is about energy. Sometimes it is about bans. Sometimes it is about a bug nobody has quite found. The quantum version is more elegant than most, which is why it sticks. It does not require a politician or a bank. It only requires a future device that can turn a public key back into a private key and sign a transaction that was never yours.
Elegant is not the same as imminent. A threat can be logically clean and still sit on the far side of engineering that does not exist yet. I have watched this particular warning return every few years, usually after a lab posts a result that sounds larger than it is. The coins, stubbornly, are still there. That does not prove the future. It does suggest we should be slower to treat a press cycle as a countdown.
What The Attack Would Actually Require
Strip the drama out and the claimed attack is simple to describe. Bitcoin transactions are authorized with digital signatures. The scheme in wide use rests on an elliptic curve, the one engineers call secp256k1. Your private key is a secret number. Your public key is a point derived from that number. Anyone can check a signature. Almost nobody, with classical computers, can walk backward from the public point to the secret.
A large enough quantum machine, running a variant of Shor’s algorithm, is theorized to make that walk possible. Not by guessing faster in the ordinary sense. By holding a huge superposition of candidate values and interfering them until the secret stands out. On paper, that breaks the discrete-log problem that protects the curve. On paper, a patient attacker who already knows a public key could forge a signature and move the coins.
Notice the conditions hiding in that sentence. The machine has to be large. It has to stay coherent long enough to finish a circuit with an absurd number of operations. It has to tolerate errors, or correct them, without the correction eating the whole advantage. And the attacker needs a public key that is already exposed, not merely an address that has never spent. Those are not footnotes. They are the job.
A threat that only works on a machine nobody has built is a forecast, not a burglary.
Where The Hardware Actually Sits
I am not dismissive of the labs. The devices are genuinely strange, in the best sense. Optical tweezers. Laser cooling. Superconducting loops. Electromagnetic traps. Dilution refrigerators that make a room feel like a joke. Individual qubits are pushed into delicate states, entangled, nudged through a computation, then read out before the environment ruins the party. That any of this works at all is a fair reason to stare.
Staring is not the same as handing over your keys. The honest status report, if you ignore the marketing layer, is that these machines still struggle with problems a sharp child could finish on paper. Useful demonstrations exist. Out-of-reach demonstrations, relative to ordinary computers, are argued over and often shrink once the classical side is allowed to be clever. Error rates remain the tax on every pretty diagram. Scale remains the wall.
Here is the part that rarely makes the headline. To run even a modest circuit on some of the leading candidate technologies, you may need the power budget of a large building’s cooling plant, hours of calibration, and more hours of classical cleanup afterward. That is not an insult. It is a stage of life. Early aircraft were also ridiculous. The difference is that flight had a clear physical path and a customer who would pay for each ugly improvement. Cryptographic breakage needs something closer to a miracle of stability, repeated millions of times, without the miracle getting bored.
Perhaps the most interesting aspect is how little the public argument tracks that gap. People hear “quantum advantage” and picture a lockpick. Engineers hear a benchmark on a narrow task, often chosen because the quantum device is good at that task and a classical machine is awkwardly posed against it. Those are not the same photograph.
Money Is Not A Timeline
The objection I hear next is always about capital. Billions are flowing into quantum research. Governments have strategies. Startups have valuations. Surely money bends the calendar.
Sometimes it does. Often it does not. Cash accelerates a technology once the underlying science is settled and the product has a buyer who can tell success from theater. Before that point, money can fund parallel dead ends with excellent slide decks. I have found that the shuttle-versus-reusable-rocket comparison is the cleanest way to see it, even if the industries differ. One program spent lavishly on a vehicle that never became cheap or routine. Another took mostly known physics, cut the ceremony, and flew because a market would pay for reliable kilograms to orbit. No budget increase on the first path was going to invent the second path. The constraint was not enthusiasm. It was the shape of the problem.
Translate that to qubits and the moral is uncomfortable. Demonstrations at enormous cost are already possible. A stable, low-error, scalable qubit that behaves more like a reliable engine than a laboratory specimen is a different object. Continued spending on today’s candidate designs may improve those designs. It may also be spent polishing approaches that never cross the threshold. We cannot know which, and pretending the funding chart is a progress chart is how forecasts go silly.
Two Kinds Of “Breakthrough”
Recent papers deserve a slower read than social feeds give them. A lot of what gets called progress lives entirely in mathematics. A circuit is reduced. A resource estimate is tightened. A theoretical attack on paper needs fewer logical operations than last year’s estimate. That work matters to specialists. It does not conjure a device.
One widely discussed result even withheld the full circuit, on the theory that publishing it might help someone misuse it later. Dramatic, yes. Also a little theatrical. Hiding a blueprint for a machine that may never be built does not move the machine closer. It changes the conversation, not the refrigerator. Until hardware has its own equivalent of a workhorse rocket, there is nothing in the lab that can run the scary version of that circuit at cryptographic scale.
Hardware papers are real too, and some of them are careful. The trouble is aggregation. A year of headlines can look like a straight road if you stack them. Look closer and they often belong to different candidate technologies, or to restarts after a previous line stalled. Neutral atoms. Superconducting circuits. Trapped ions. Photonics. Each has a faction, a metric it wins, and a metric that embarrasses it. Progress inside one family is not progress for the field in the way a casual reader assumes.
I tend to watch neutral-atom work with more curiosity than the rest, mostly because the control story feels less tortured. That is a preference, not a prediction. It is far too early to claim a path is open all the way to a code-breaking machine, along that branch or any other. If we ever see the same architecture iterated, year after year, into devices that compute things a precocious student cannot also compute, then the conversation should change. We are not there.
- Math results can shrink a future circuit without creating a qubit.
- Hardware results often restart rather than stack.
- Different qubit families do not add up into one machine.
- A redacted diagram is not a prototype.
- Funding proves interest, not feasibility.
The Scale Nobody Puts On A Slide
Talk to people who estimate resources, not people who estimate headlines, and the numbers get rude. Breaking elliptic-curve signatures at Bitcoin’s security level is not a matter of a few hundred noisy qubits and a long weekend. Credible estimates, even the optimistic ones, talk about millions of physical qubits once you account for error correction, or logical qubits in quantities no lab has approached, running for lengths of time that make today’s coherence look like a blink.
Estimates move. They should. Better codes, better gates, cleverer layouts, all of that can cut the bill. Cutting the bill from “absurd” to “still absurd” is not the same as arriving. I keep a simple rule for myself: if the machine required is several orders of magnitude beyond the best device on Earth, the calendar in the headline is a mood, not a measurement.
There is also a quieter theoretical unease that rarely gets airtime. To be cryptographically relevant, a quantum machine has to represent a possibility space as large as the problem. For the 128-bit security level associated with this curve, that means a superposition spanning a field the size of a 128-bit space. Classically, storing every candidate would demand more memory than humanity has ever fabricated, by a margin that is almost comic. Quantum mechanics is supposed to dodge that by not storing them classically. Fine. But if the superposition has any meaningful grain, any floor beneath which values are not truly distinct, the dodge fails. If the energy needed to hold that superposition grows with the size of the field, the dodge may fail in a different way. Contemporary physics does not politely rule those possibilities out. It also does not confirm them. The point is narrower: impossibility is still on the table, and so is “possible, but not on any budget we can name.”
A rough mental model, not a lab specification:
  Known devices: dozens to low thousands of physical qubits
  Error-corrected logical qubits today: a handful, on a good day
  Estimated need for curve breakage: vast, after correction overhead
  Gap: not a product cycle, a different era of engineering
Why The Story Keeps Winning Anyway
Narratives do not need a working device. They need a villain with a calendar. Quantum computing supplies both, plus a vocabulary most readers will not challenge. That is catnip for a market that already argues about everything. A dip in price can be blamed on the machines. A rally can be blamed on the machines being late. Either way the story gets another lap.
I do not think most of the people repeating it are lying. Many are pattern-matching. They saw one technology arrive faster than experts swore it would, so they assume every hard technology will. Smartphones did that. So did certain kinds of machine learning. The mistake is treating “sometimes experts are slow” as “every physics constraint is optional.” Some constraints are social. Some are thermodynamic, or about noise, or about the ugly fact that error correction multiplies your hardware instead of shrinking it.
There is a status game in it too. Warning about a distant catastrophe sounds more serious than saying the lab photos are ahead of the capability. Seriousness is not evidence. If you have sat through enough cycles of this asset, you learn to separate a risk that can empty a wallet this month from a risk that lives in a keynote.
What Is Exposed, And What Is Not
Even in the hypothetical where a relevant machine appears, Bitcoin does not become a single glass box. The protocol reveals public keys at specific moments. An address that has never spent typically publishes a hash, not the raw public key. Spending reveals more. Reused addresses reveal more still. Coins sitting in older output types are not all equally easy to describe in an attacker’s notebook.
That nuance gets flattened into “quantum steals Bitcoin,” which is handy and wrong. A future attacker would triage. Exposed keys first. Dormant outputs with known keys next. Anything still behind a hash would need an extra step, and time, and a mempool that does not simply reject a suspicious spend. None of this is a shield forever. It is a reason the cartoon of instant global theft does not match how the system is built.
Lost coins are the part of the story people whisper about, because the keys are gone and the public material may already be sitting on chain. In a genuine future attack those outputs are the awkward inheritance. They are also not your hot wallet, and they are not a reason to pretend the attack exists now. Conflating a someday problem for abandoned outputs with a today problem for careful custody is how fear gets a bigger audience than it earned.
| Claim you will hear | What the evidence supports | Practical stance |
| A lab result means keys fall next year | Results are narrow, noisy, and often classical-competitive | Read the qubit count and the error rate, not the verb |
| Funding guarantees a code-breaker | Money speeds known paths, not unknown physics | Treat budgets as interest, not a date |
| Every coin is equally exposed | Key reveal depends on address use and output type | Stop reusing addresses regardless |
| Upgrades are pointless until the machine exists | Migration takes years even if the threat is late | Follow signature research without panic |
| Quantum risk is the main custody risk | Phishing, bad backups, and sloppy key reuse dominate | Fix the risks that already have victims |
The Long Argument For Preparing Anyway
Here is where I part ways with pure dismissal. Saying the machine is not close is not the same as saying cryptography should freeze. Curves have been broken before, for boring mathematical reasons that had nothing to do with qubits. Parameters that looked fine aged badly. Implementation bugs have embarrassed systems that were elegant on a whiteboard. Bitcoin has lasted because pressure, real or imagined, forced sharper engineering. That habit is worth keeping.
Post-quantum signatures are a crowded workshop. Hash-based schemes. Lattice-based schemes. Variants that try to keep verification cheap enough for a decentralized network, which is the constraint polite white papers forget. A signature that a nation-state server can check in a millisecond may still be a poor fit if every node on Earth has to check it, store it, and gossip it. Size matters. Speed matters. Assumption quality matters. So does the politics of a migration, because coins do not move themselves to a new script type.
Work on newer output designs, on hash-based fallbacks, on lattice signatures, on hybrid constructions that do not ask everyone to bet the network on one fresh assumption, is healthy even if a relevant quantum computer never arrives. I would rather see that work proceed in public, with ugly benchmarks, than watch it get rushed by a headline. Panic produces bad parameters. Boredom produces none. The middle path is unglamorous and correct.
Prepare as if migration will take longer than the scare, and longer than the optimists in the lab admit.
A custody rule worth keeping
Migration Is The Actual Hard Problem
Suppose, for the sake of stress-testing the fear, that a credible prototype appears in the 2030s. Not a blog chart. A device that informed skeptics agree can threaten real keys, with a timeline measured in years rather than press cycles. What happens then is not a weekend patch. It is a social migration.
Holders would need a new address type, wallets that can spend to it, exchanges and custodians willing to support it, and a window long enough for coins to move. Some coins will not move, because the owners are gone, or the keys are lost, or the operational burden is ignored until too late. That is a governance and communication problem as much as a math problem. Networks that wait for perfect consensus discover that perfect consensus is a synonym for delay.
This is why early research is not hypocrisy. You can believe the machine is distant and still want the escape hatch designed before anyone is shouting. Aircraft carry life rafts without expecting to ditch on a clear Tuesday. The raft does not mean the ocean is in the cabin.
- Agree on schemes that nodes can actually verify at scale.
- Ship wallet support before any panic window opens.
- Give holders a boring path to move coins, not a heroic one.
- Treat abandoned outputs as a separate policy question.
- Refuse timelines invented to match a news cycle.
The Risks That Already Have Victims
If I am blunt about priority, quantum sits below a pile of dull threats that have already taken coins. Phishing pages. Fake support accounts. Seed phrases photographed “for backup.” Address reuse. Malware that waits for a clipboard. Custodians with charming apps and thin controls. Those are not theoretical. They invoice people every week.
A quantum scare can even make those worse. Someone anxious about a distant machine is easier to rush into a “quantum-safe wallet” run by a stranger, or into a migration service that asks for the seed. I have seen fear used as a funnel more than once. The costume changes. The ask does not. If a fix requires you to type your recovery words into a website, it is not a fix.
Good hygiene is unfashionable because it does not trend. Use outputs that do not reveal more than they must. Do not reuse addresses. Keep long-term storage offline. Test a recovery before you need it. Prefer schemes and wallet software with years of hostile attention, not a landing page born last quarter. None of that stops a future physics breakthrough. All of it stops the attacks that exist on a Tuesday.
How To Read The Next Announcement
There will be another paper. There always is. When it lands, a few questions cut through the adjectives.
How many physical qubits, and of what quality? What error rate, and was it maintained during the run or quoted from a calmer moment? Is the result a logical qubit doing useful work, or a physical qubit in a demo? Which technology family is this, and does it continue a previous line or start over? What classical algorithms were used as the comparison, and were they given a fair afternoon? If the claim is cryptographic, where is the resource estimate for a full break, including correction overhead, not for a toy instance?
You do not need a physics degree to ask those. You need a refusal to let the verb “breakthrough” do the thinking. In my experience, announcements that survive those questions are rarer than announcements that do not. The rare ones are worth your attention. The others are worth a shrug and a return to custody basics.
Announcement filter:
  qubit quality > qubit headline
  full resource estimate > toy circuit
  same architecture, repeated > one-off demo
  independent replication > vendor blog
A Note On Certainty, Including Mine
I should be plain about the limit of this view. Absence of a machine is not a proof that a machine is impossible. Physics has embarrassed confident skeptics before. It has also embarrassed confident boosters, more often, once the press conference ended and the error bars remained. The honest position is a range. A relevant quantum computer might arrive later this century. It might stall for reasons we can already sketch. It might require an architecture nobody in the current race is holding.
What the evidence does not support is a near-term theft story. No public device computes beyond a gifted child in any way that threatens a Bitcoin key. No funding round has changed that sentence. No redacted circuit has changed it either. If that sentence becomes false, it will become false in measurements first, in headlines second. Watch the measurements.
There is a human temptation, once you have decided a fear is overstated, to mock anyone who still researches the defense. Resist it. The people designing post-quantum signatures are not the same people selling panic. Some of them are doing the slow work that makes a future migration possible without a stampede. Skepticism about timelines and respect for that work can live in the same head. They should.
What Holders Can Ignore, And What They Should Not
Ignore countdowns that name a year without a device attached. Ignore screenshots of roadmaps from companies whose product is the roadmap. Ignore anyone who equates a mathematical improvement with a break-in. Ignore the implication that price volatility is a quantum referendum. Markets shake for cheaper reasons.
Do not ignore address reuse. Do not ignore the difference between a hashed address and a revealed key. Do not ignore software that asks you to “upgrade” by surrendering control of the seed. Do not ignore the fact that a real migration, if it is ever needed, will be slow, public, and full of tradeoffs about signature size and verification cost. Those tradeoffs are where the serious argument lives. The cafe-table version skips them because they do not fit on a phone screen.
I keep coming back to a small distinction that clarifies most of this. Cryptographic relevance is a threshold, not a vibe. Below it, quantum machines can be fascinating and still irrelevant to your coins. Above it, the network has a practical problem and a political one. We are below it. The distance is not a rounding error.
The Shape Of A Real Warning
If I were designing the warning that should actually move behavior, it would not look like the current one. It would name a device class, a sustained logical-qubit count, an error-corrected runtime, and a published resource estimate that more than one research group accepts. It would separate exposed keys from unspent hashes. It would give wallet authors a concrete script type to implement, with sizes and fees attached, so the advice is operational rather than atmospheric.
Until that warning exists, the atmospheric version is doing a different job. It fills a silence. It gives commentators a future to point at when the present is merely volatile. It lets a difficult science wear the costume of an urgent security bulletin. Costume is the right word. Under it, the work is still early, branched, and full of restarts.
None of this makes the underlying physics fake. Superposition is not a marketing term. Entanglement is not a metaphor someone invented for a keynote. The labs are doing hard things in cold rooms, and some of those things will matter for chemistry, materials, or optimization long before they matter for signatures. That is a perfectly good reason for the field to exist. It is a poor reason to treat your wallet like it has already been copied.
A Calmer Way To Hold The Question
So where does that leave an ordinary holder who does not want a second career in qubit physics? With a shorter list than the internet offers. Keep custody boring. Prefer designs that minimize unnecessary key exposure. Follow signature research the way you follow any slow upgrade, with patience for benchmarks and suspicion of slogans. Assume that if the ground ever truly shifts, you will hear it as a change in what machines can do, repeated by people who disagree with each other, not as a single viral chart.
I still think about that cafe conversation. The phone, the headline, the certainty. Certainty is cheap when the machine is someone else’s problem and the coins are yours. The more time I have spent with the actual state of the art, the less the certainty fits. We have remarkable prototypes and a missing threshold. We have money and no Falcon-like moment for low-error scale. We have papers that advance the map and hardware that keeps discovering the map was optimistic.
Bitcoin does not get to rest on that. No durable system does. Curves can age. Implementations can fail. A future architecture could surprise everyone who wrote a calm essay in the middle of the decade. The response to that possibility is continued work on resilient signatures and a migration path that does not require heroics. The response is not to pretend the burglar is already in the hall.
Fear will be back. It always is. Next time it arrives with a new figure and an old conclusion, ask what the machine computed, how long it stayed coherent, and whose coins it could actually reach. If the answers are still “a small problem,” “not long,” and “none of them,” you can close the tab. The coins were never waiting on the headline. They were waiting on the physics, and the physics has not caught up.
]]>