
Ever wonder how a single fake meeting invite can ripple through a crypto trading platform and force major exchanges to pull the plug on API connections overnight? That is exactly what unfolded for SignalPlus in the early hours of November 4. The platform, which helps professional and institutional traders manage options and derivatives across multiple venues from one interface, found itself dealing with a contained but very real intrusion. Losses stayed under $82,000. Still, the episode left clear lessons about vendor access, employee devices, and the quiet importance of something as basic as IP whitelisting.
How a Compromised Telegram Account Opened the Door
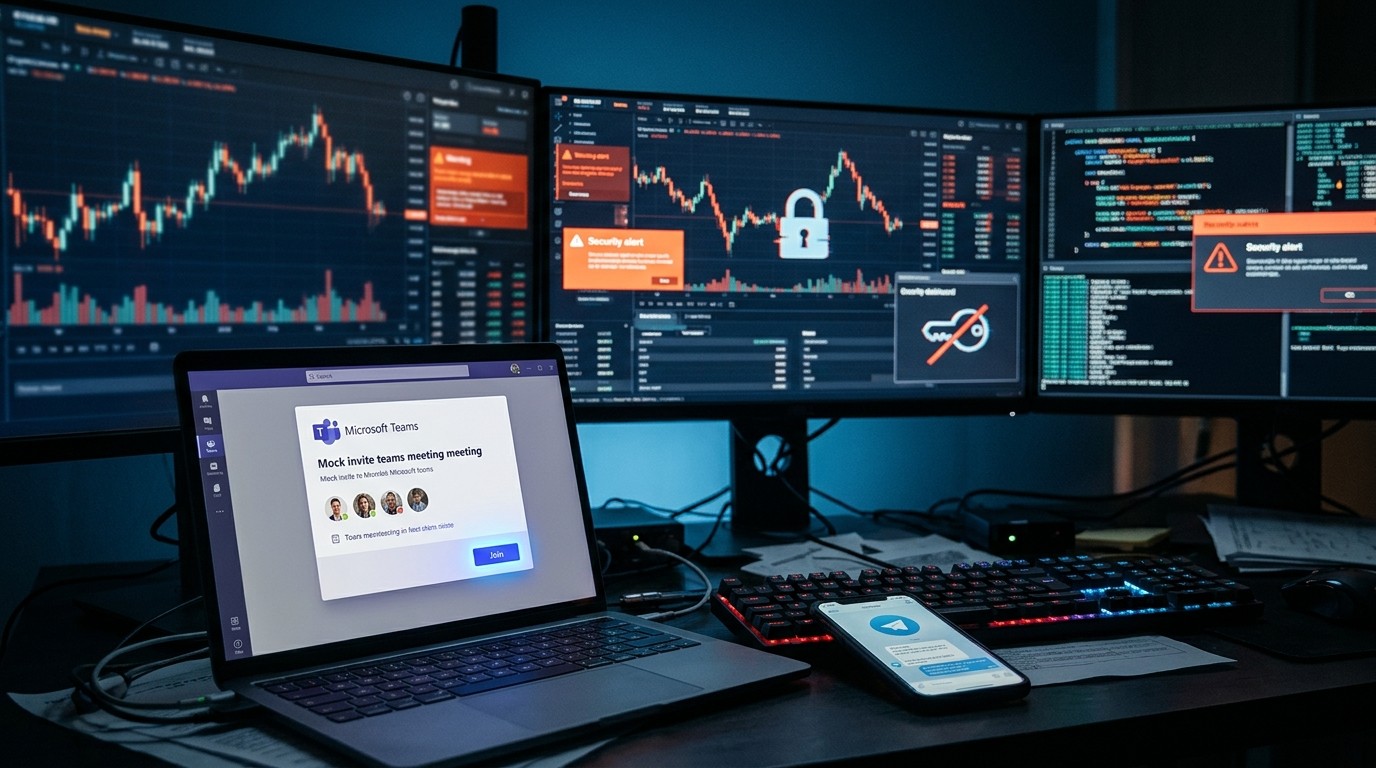
The attack did not start with sophisticated zero-day exploits or flashy on-chain maneuvers. It began with a third-party technology vendor contact whose Telegram account had already been taken over. The attacker used that account to pose as the familiar contact and sent a SignalPlus engineer a seemingly legitimate Microsoft Teams meeting invitation. Once the engineer interacted with it, the machine was compromised. The intruder then stayed quiet for a stretch, waiting for the right moment.
In my experience covering these incidents, that quiet period is often the most dangerous part. The attacker sits on the access, maps the internal network, and only moves when conditions look favorable. Early on November 4 the activity ramped up. SignalPlus teams spotted the unusual behavior quickly, blocked further progress, and shut down the pathways the attacker had used. They also reached out to their exchange partners so connected customer credentials could be disabled as a precaution.
What stands out is how ordinary the entry point looked. A trusted name on Telegram. A routine meeting request. Many of us click through those without a second thought during a busy trading day. That is why the platform later admitted the real gap sat closer to home: it had never made IP whitelisting mandatory for the exchange API keys its users connected. That single missing control left a small number of accounts exposed once the internal foothold was established.
The Role of Missing IP Whitelisting
IP whitelisting is straightforward in concept. It limits an API key so it can only be used from pre-approved internet addresses. When that control is optional rather than required, an attacker who gains control of a machine or a set of credentials gains far wider latitude. SignalPlus has been open about this point. The company stated it takes responsibility for the oversight and is now tightening the requirement across the board.
I’ve found that platforms sometimes leave such settings optional because they want to keep onboarding friction low for institutional clients who operate from multiple locations or use rotating cloud infrastructure. The convenience is real. The risk becomes visible only after an incident. In this case the absence of mandatory whitelisting meant a handful of accounts without the extra layer were the ones that saw activity. Everyone else remained outside the immediate impact zone, yet the exchanges still chose to revoke the broader set of SignalPlus-linked keys as a blanket safety step.
We take responsibility for this oversight.
That sentence from the platform’s own statement carries weight. Admitting the gap publicly is better than trying to bury it under technical jargon. It also sets a clearer expectation for what comes next: stronger controls on development devices, tighter internal access rules, better key management practices, and deeper information sharing with exchanges and security partners.
Exchange Response and User Impact
Binance and Deribit both moved quickly once they received the notification. They revoked the API keys associated with SignalPlus. Both exchanges stressed that their own systems and customer funds stayed untouched. The revocations were purely precautionary. Trading, monitoring, and automation that previously ran through the SignalPlus interface simply stopped working for the affected customers until new connections could be established safely.
Users were advised to manage positions and open orders directly on the exchange platforms in the meantime. That advice is practical. Disabling an API key does not mean the underlying account or assets have been compromised. It simply removes one pathway an attacker might have used. SignalPlus emphasized this distinction so that customers would not panic and liquidate positions unnecessarily while the platform remained in maintenance mode.
Reimbursements started almost immediately on a case-by-case basis. Anyone who believes they incurred losses was invited to contact the company for verification and repayment. The total figure stayed under $82,000, which is modest by the standards of recent crypto incidents, yet every dollar still matters to the people who lost it. The platform’s decision to cover the shortfall in full is the right move if trust is to be restored.
Timeline of Detection and Containment
The sequence unfolded over a relatively short window. Suspicious activity was noticed in the early hours of November 4. The team contained the intrusion the same day, identified the entry vector, and coordinated with exchange partners. By November 5 the public statement was out, services sat in maintenance, and the reimbursement process had already begun for verified cases.
Speed mattered here. The longer an attacker remains inside a network, the more opportunity exists to escalate privileges or move laterally. By acting before the damage spread further, SignalPlus limited both the financial impact and the number of accounts touched. That does not erase the fact that an employee device was compromised in the first place, but it does show that detection and response processes were functional once the activity became visible.
Perhaps the most interesting aspect is how the attacker remained dormant after the initial compromise. That patience suggests a degree of planning rather than opportunistic smash-and-grab behavior. It also underscores why endpoint protection and continuous monitoring of privileged devices remain critical even when the primary business is trading infrastructure rather than custody of large asset pools.
What Changed for Customers During Suspension
While SignalPlus kept its own services offline for review and patching, customers retained full access to their exchange accounts through the official interfaces. Positions could still be monitored. Orders could still be adjusted or closed. The only missing piece was the unified interface and any automated strategies that relied on the SignalPlus connection.
This separation is worth noting. Many third-party trading tools sit on top of exchange APIs rather than holding the assets themselves. When the tool is taken offline, the underlying accounts continue to function. The inconvenience is real for traders who built workflows around the single dashboard, yet the core funds stay where they always were. That architecture limited the blast radius of this particular event.
- Direct exchange logins remained fully operational
- API-based automation through SignalPlus stopped until reconnection
- Open orders and positions stayed visible and manageable on the native platforms
- Users were encouraged to enable IP whitelisting on any new API keys they create
Those practical steps gave customers a clear path forward even while the platform completed its internal work. The phased return of services, expected over the following days once patches and reviews finish, should restore the familiar interface once the team is confident the environment is clean.
Broader Lessons for Third-Party Trading Tools
Incidents like this keep highlighting the same set of recurring themes. Third-party platforms that sit between traders and exchanges become attractive targets precisely because they hold aggregated access. An attacker who compromises one of them can potentially reach many customer keys at once. The defense therefore has to be multi-layered: strict vendor access controls, hardened employee devices, mandatory network restrictions on API keys, and rapid coordination channels with the exchanges themselves.
In my view the social engineering vector remains underestimated. People still trust familiar names on messaging apps. A well-timed meeting invite that looks like it comes from a known contact can bypass a surprising number of technical defenses. Training helps, but so does reducing the privileges available on any single device and enforcing network-level restrictions that survive even if a machine is taken over.
SignalPlus has outlined a set of planned improvements that address exactly these areas. Stronger requirements around API access, better protection for development machines, improved internal access management, revised key handling procedures, and closer collaboration on threat intelligence with partners. Those steps are necessary. Whether they prove sufficient will only become clear over the coming months of normal operation.
Why the Loss Figure Stayed Limited
Several factors kept the financial damage under $82,000. Detection happened early. The number of accounts lacking IP whitelisting was small. The attacker did not appear to gain the ability to move large volumes before the response kicked in. And the platform itself moved to reimburse verified losses rather than leave customers absorbing them.
That combination is better than many recent episodes where the first public number runs into the tens or hundreds of millions. Still, the absolute size of the loss should not distract from the underlying control failure. A missing mandatory safeguard allowed the intrusion to produce any financial impact at all. Closing that gap is the more lasting takeaway.
Traders who rely on similar aggregation tools should treat this as a prompt to review their own setups. Confirm that every exchange API key is restricted by IP where the platform supports it. Prefer keys with the narrowest possible permissions. Keep an eye on the official status channels of any third-party service you depend on. And maintain the ability to trade directly on the exchange if the intermediate layer ever goes offline.
The Path Back to Normal Operations
SignalPlus indicated that services would return in phases after a full security review, necessary patches, and confirmation that operations could resume safely. Progress updates and customer instructions would come through official channels. The investigation itself continues, and the company has invited ongoing user feedback during the process.
Phased restoration is the prudent approach. Bringing everything back at once after an intrusion can reintroduce risk if any residual access path remains. By staging the return, the team can monitor for anomalies at each step and still give customers incremental access rather than an all-or-nothing wait.
For most users the practical effect will be temporary inconvenience rather than permanent loss. The reimbursements cover the financial side. The security upgrades aim to reduce the chance of a repeat. And the exchanges’ decision to revoke keys, while disruptive in the moment, demonstrated that the surrounding ecosystem can still respond when a partner reports a problem.
Practical Steps Traders Can Take Right Now
Even if you never used SignalPlus, the episode offers a useful checklist. First, review every API key you have created on major exchanges. Confirm whether IP whitelisting is enabled and whether the allowed addresses still match your current setup. Second, audit the permission levels on those keys. Many platforms allow keys that can only read data or place orders but cannot withdraw. Prefer the most restricted option that still meets your needs.
Third, treat any unexpected meeting invite or message from a vendor contact with extra caution, especially if it arrives on a secondary messaging app. A quick verification through a second channel costs little and can stop an attack before it starts. Fourth, keep the ability to manage positions directly on the exchange. Relying exclusively on any single third-party interface creates a single point of failure when that interface is taken offline for security reasons.
- Enable IP restrictions on every active exchange API key
- Limit key permissions to the minimum required for your strategy
- Verify unexpected meeting requests through a second channel
- Maintain direct exchange access as a fallback
- Monitor official status channels of any intermediate platforms you use
Those habits will not eliminate every risk, but they raise the bar an attacker has to clear. In a market where social engineering continues to succeed against even well-resourced teams, the extra friction is worth the protection.
Looking Ahead for Aggregated Trading Platforms
The demand for unified interfaces that sit across multiple exchanges is not going away. Professional traders value the ability to see positions, risk, and opportunities in one place. The platforms that provide that convenience will keep attracting users. They will also keep attracting attention from attackers who see concentrated access as an efficient target.
The difference between a minor incident and a catastrophic one often comes down to the controls that were already in place before the first phishing message arrived. Mandatory network restrictions, rigorous vendor access management, continuous monitoring of privileged endpoints, and practiced coordination with exchange partners all reduce the window of opportunity. SignalPlus has now committed to strengthening those areas. Other platforms would do well to examine their own setups against the same checklist without waiting for a similar wake-up call.
I’ve noticed that the most resilient operations treat security as an ongoing process rather than a one-time project. They test their response plans. They rotate credentials on a schedule. They assume that some device will eventually be compromised and design the rest of the system so that compromise does not automatically translate into widespread financial loss. That mindset is harder to maintain when the primary focus is shipping features and onboarding new institutional clients, yet it is exactly the mindset this incident reinforces.
Final Thoughts on Containment and Responsibility
The SignalPlus episode could have been far worse. Early detection, limited exposure from the missing control, rapid exchange cooperation, and a clear reimbursement commitment kept the damage contained. The platform’s willingness to state publicly that it had left IP whitelisting optional is also a positive signal. Ownership of the gap is the first step toward closing it.
For the broader market the message is familiar yet still necessary. Social engineering remains effective. Third-party access layers introduce additional attack surface. Basic network controls that many teams treat as optional can become the difference between a small reimbursement pool and a much larger crisis. Traders and platforms alike benefit when those controls move from optional to expected.
Services are expected to return over the coming days once the review and patches are complete. Users who experienced losses have a path to recovery. And the rest of the ecosystem has another concrete example of how a single compromised messaging account can cascade into revoked API keys and temporary platform downtime. The details may fade, but the underlying lessons should not.
In the end the numbers stayed modest, the response was relatively swift, and the platform has outlined a concrete set of improvements. That combination offers a better outcome than many recent security events in the space. Whether the upgrades hold under future pressure will be the real test. For now the priority for affected users is verifying any losses, managing positions directly on the exchanges, and waiting for the official all-clear before restoring the previous connections.
The story also serves as a quiet reminder that even specialized trading infrastructure is only as strong as its weakest human and technical link. A familiar name on Telegram, a routine meeting invite, an employee device without sufficient isolation, and an optional rather than mandatory network restriction proved enough to create a real incident. Closing each of those gaps is the work that remains. The fact that the financial impact stayed under $82,000 is fortunate. Relying on fortune is not a sustainable security strategy.
As the platform moves through its phased restoration, the rest of the market can treat the episode as a free stress test of their own assumptions. Check the settings. Verify the channels. Keep the fallback options ready. Those steps cost little compared with the alternative of discovering the gaps only after an attacker has already moved.