
Imagine sending a large amount of stablecoins and realizing only minutes later that the money went to a complete stranger. That is exactly what happened to one USDT holder who lost roughly fifty thousand dollars in a single transaction on Ethereum. The address looked familiar. The first few characters matched. The last few matched too. Yet it was a carefully crafted fake designed to sit quietly in the transaction history until the moment the victim needed it.
How Address Poisoning Quietly Steals Crypto Funds
Address poisoning is not a flashy hack that breaks into wallets or exploits smart contract bugs. It is quieter and, in many ways, more dangerous because it relies on human habits. Most people who move crypto regularly end up copying addresses from their own past transactions. They trust what already appears in their history. Attackers know this and work hard to place a nearly identical address right there in the list.
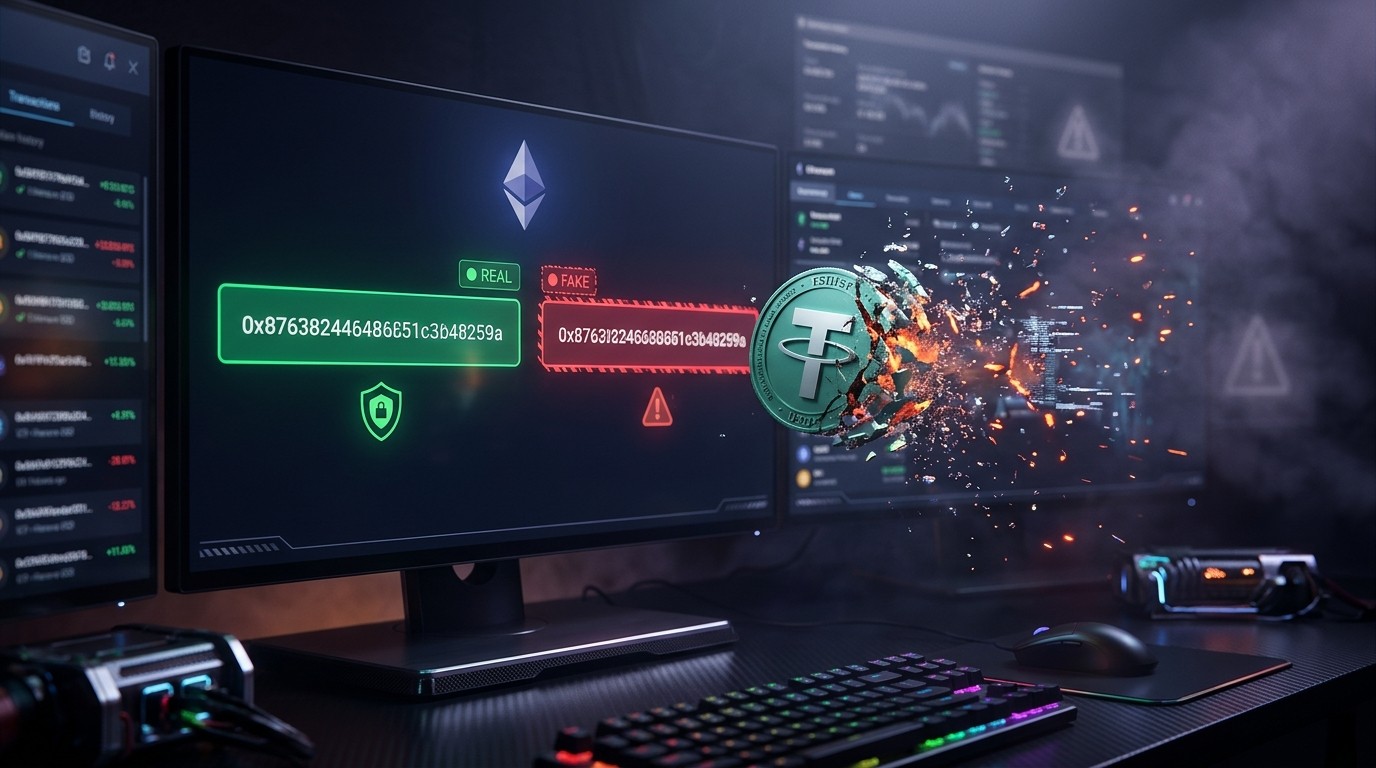
The process usually starts when someone monitors transfers of popular tokens, especially stablecoins like USDT. Once a target is identified, the attacker generates a new address that shares the same opening characters and the same ending characters as a real address the victim has used before. Then a tiny amount of tokens, sometimes even a zero-value transfer, is sent to the victim. That small transaction plants the lookalike address firmly in the activity feed.
Later, when the victim decides to send a larger amount, the poisoned address sits right there looking trustworthy. In the recent case, the fraudulent address matched the intended recipient’s first four and last six characters. That level of similarity is enough to fool most people who only glance at the shortened version displayed by many wallets and explorers.
Why Shortened Addresses Make the Trap So Effective
Wallet interfaces often display only the beginning and the end of a long Ethereum address. The middle section gets hidden behind dots or simply cut off. When the visible parts look correct, the brain fills in the rest and assumes everything matches. I’ve seen this pattern play out more times than I care to count, and it still surprises me how often smart people fall for it.
The middle of the address is where the real difference lives, yet almost nobody scrolls or expands the full string every single time. That small convenience becomes the opening the scammer needs. Once the funds leave the wallet, recovery becomes extremely difficult because the attacker usually moves the stablecoins into other assets quickly to reduce the chance of any freeze.
A Closer Look at Recent Cases and Patterns
This latest fifty-thousand-dollar loss is not an isolated event. Earlier incidents followed almost the same script. In one notable case, a user lost around one hundred thousand USDT after selecting an imitation address that had been sitting in the wallet history for sixty-six days. The attacker had planted it long before and simply waited.
In another instance, a trader first sent a small test payment of fifty USDT to the correct address. Shortly afterward an attacker inserted a dust transaction of only a few cents into the history. The lookalike matched the first three and last four characters of the real destination. When the large remaining balance of nearly fifty million USDT was transferred, it went straight to the wrong place. The funds were later converted into ETH and spread across multiple wallets, with some portions moving through mixing services.
These stories share the same core mistake: treating transaction history as a reliable address book. It is not. Every address in that list needs independent verification, especially when large amounts are involved.
What Wallet Providers Are Doing About It
Some wallet developers have started adding protections. One major provider now compares a proposed destination against addresses already present in the user’s history. If the new address looks too similar to a previous one, a blocking warning appears before the transaction can be confirmed. The system checks for matching first and last characters while noting differences in the middle section.
Another warning triggers when funds are about to be sent to an address the user has never interacted with before. That does not automatically mean the destination is malicious, of course, but it forces a moment of pause. The same provider strongly recommends saving verified addresses in a contacts list rather than relying on recent activity.
Hardware wallet makers have also issued clear guidance. They point out that an unsolicited incoming transaction or NFT does not move anything out of the account by itself. The user still has to initiate and sign an outgoing transfer. Their advice is straightforward: hide unwanted tokens and NFTs from the interface and never interact with suspicious assets or the addresses tied to them.
The Role of Blockchain Explorers in Spreading the Problem
Blockchain explorers can accidentally amplify address poisoning. When every tiny transfer appears in the public history, the poisoned address gains visibility. Some explorers hide zero-value transfers by default, while others require users to turn on a filter manually. Industry voices have called for better default filtering of obvious spam transactions so that legitimate users are less likely to encounter the traps.
At the same time, filtering carries its own risks. Very small payments between automated systems or AI agents could get hidden alongside the malicious ones. Finding the right balance is still an open conversation among developers and security researchers.
Practical Steps That Actually Reduce the Risk
After watching these incidents accumulate, a few habits stand out as genuinely useful. First, never copy an address from transaction history when sending a meaningful amount. Always pull the address from a trusted source such as a saved contact or a verified message from the recipient.
Second, when you do need to check an address, expand the full string and compare every single character. It takes a few extra seconds. Those seconds are cheaper than losing five figures.
Third, send a tiny test transfer first and confirm receipt through an independent channel before moving the bulk of the funds. Many people already do this, yet they still sometimes copy the wrong address for the second transfer. The test itself does not protect you if the address you paste next is the poisoned one.
Fourth, keep a clean contacts list inside the wallet. Once an address has been verified multiple times and used successfully, save it under a clear label. That simple practice removes the temptation to dig through history under time pressure.
- Always expand and compare the full address character by character
- Save verified destinations in your wallet contacts
- Use a small test transfer and confirm via a separate channel
- Enable any available lookalike address warnings in your wallet
- Hide unsolicited tokens and NFTs so they do not clutter the interface
These steps sound basic, yet they would have prevented the majority of the losses described above. The technology side is improving, but the final line of defense remains the person holding the private keys.
Why Stablecoins Remain a Favorite Target
Attackers prefer USDT and similar stablecoins for a simple reason. The value stays relatively constant, so the stolen amount does not swing wildly while they move it. Once the funds arrive, converting them into ETH or other assets and spreading them across fresh wallets reduces the chance that any issuer or exchange will freeze the original tokens in time.
Stablecoins also move frequently between traders, market makers, and ordinary users. That volume creates more opportunities for monitoring and planting poisoned addresses. High activity equals more potential victims.
The Psychological Side of the Scam
Perhaps the most interesting aspect is how little technical skill the victim needs to fail. The attack succeeds because of trust in the interface and the desire to move quickly. Under pressure, or simply out of habit, people take shortcuts. The scammer only needs to make the shortcut look safe.
In my experience, the users who escape these traps are the ones who treat every large transfer as a deliberate process rather than a routine click. They double-check even when the address looks familiar. That mindset is harder to adopt than any new wallet feature, yet it remains the strongest protection available today.
What Happens After the Funds Are Gone
Recovery is rare. Once the transaction is confirmed on the blockchain, reversing it requires the cooperation of the attacker or intervention from a centralized entity that controls the tokens. In most of the documented cases the stolen USDT was quickly swapped and distributed. Some victims have posted on-chain messages offering bounties for the return of a large percentage of the funds. Results vary, and many never recover anything.
The emotional impact is often underestimated. Losing a significant sum through a simple copy-paste error creates a particular kind of frustration. The knowledge that the money is still sitting somewhere on the same network, just under someone else’s control, makes the loss feel sharper.
Looking Ahead: Better Tools and Persistent Habits
Wallet software will keep improving. More aggressive similarity checks, clearer full-address displays, and smarter filtering of spam transactions should reduce the number of successful attacks over time. Explorers may also refine how they present history so that dust transactions become less visible by default.
Still, no tool can completely eliminate the risk while users continue to rely on visual similarity and past activity. The fifty-thousand-dollar loss reported this week is a fresh reminder that the basic habits matter more than any single software update.
Address poisoning will probably remain part of the crypto landscape for years. The cost of generating a lookalike address is low, the potential payoff is high, and human behavior changes slowly. The best defense is a combination of better interfaces and disciplined personal practice.
If you move stablecoins regularly, take a moment today to clean up your contacts list and review how you currently select destination addresses. The next transfer you prepare might be the one that tests whether those small habits are already in place.
The story of the recent USDT loss is straightforward on the surface, yet it reveals deeper truths about how we interact with blockchain interfaces. Convenience and security often pull in opposite directions. Every time a wallet shortens an address for readability, it creates a tiny opening. Every time a user copies from history instead of a verified source, that opening widens.
Security researchers continue to track these campaigns and share patterns so the community can adapt. The more people understand the exact mechanics, the fewer successful traps will be set. Education remains one of the few tools that scales across every wallet and every chain.
In the end, the responsibility sits with the person holding the keys. No warning dialog can replace careful verification. No explorer filter can replace the decision to expand the full address and read it character by character. Those extra seconds are the difference between a routine transfer and a permanent loss.
Stay deliberate. Double-check the parts that look the same. Save the addresses you trust. And remember that the most convincing fake is the one that already lives inside your own transaction history.
That is the quiet danger of address poisoning. It does not announce itself with flashing red lights. It simply waits, looking almost right, until the moment you need it least.