
I still remember the first time I watched a validator miss a block because of a simple config mistake. That small moment cost real money. So when news broke that a certificate vulnerability could let someone quietly redirect Ethereum rewards, my stomach dropped a little. This wasn’t theoretical. It touched the exact systems many stakers rely on every day.
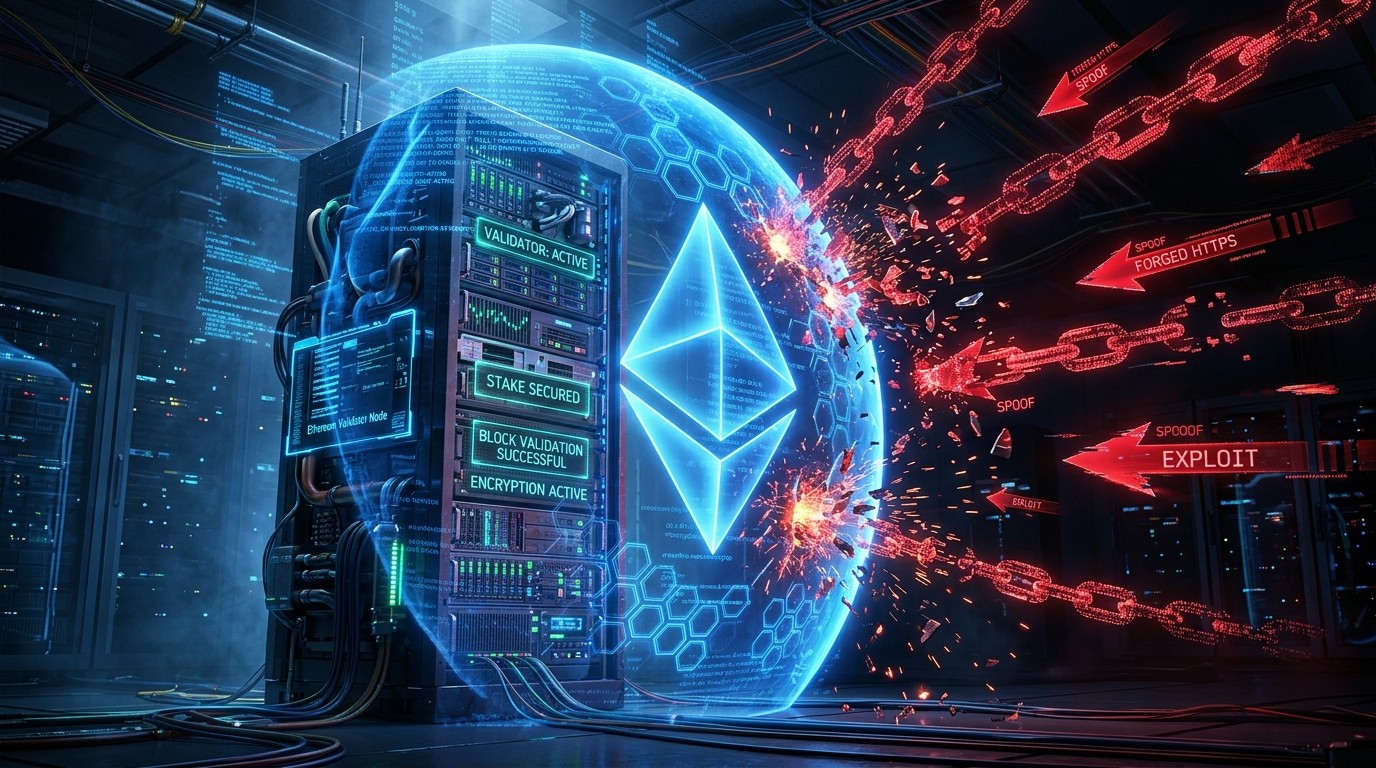
Two major Ethereum clients, Teku and Besu, moved fast. They pushed security updates after discovering that weak cryptographic keys from a certificate authority could allow attackers to impersonate trusted services. In the right conditions, that impersonation might trick a validator into sending its block rewards somewhere else. Default setups were mostly safe, yet plenty of operators run custom or external connections. Those people needed to act.
What Exactly Happened With the Certificate Flaw
The root of the problem sat with eight intermediate certificate authorities run by an Indian provider. Their private keys had been generated with far too little randomness. Once researchers looked closely, the keys could be recovered from public information alone. That discovery landed in mid-October. By the 18th the certificates were revoked. Technology companies started scrubbing trust for them. Windows received updates. Yet Java, the runtime that powers both Teku and Besu, does not check revocation lists by default. Old trust lingered.
In practical terms this meant an attacker who could intercept traffic might present a forged certificate that still looked legitimate to an unpatched Java environment. The validator software would accept the connection. From there the possibilities grew uncomfortable.
How an Attacker Could Redirect Rewards
Picture a validator that talks to a remote beacon node over HTTPS. If someone sits in the middle and waves a fake but trusted certificate, the validator might receive altered instructions about the block it is about to propose. Transaction fees could be steered toward an address the attacker controls. That is the nightmare scenario the advisory spelled out.
External signing services presented another risk. Many operators keep their validator keys on a separate machine or service for safety. An attacker impersonating that signer could, under certain setups, request signatures for exits or other sensitive actions. Mutual TLS would reduce the damage to a simple denial of service, but not every installation uses it.
Other connections sat in the danger zone too: execution clients, block builders, relays, and any service that pulls configuration data. The peer-to-peer network itself stayed untouched because it never relied on those particular certificates. Still, the surface area was large enough to worry anyone running non-default infrastructure.
Default mainnet configurations were not affected and no exploitation has been reported so far.
That statement from the developers is reassuring. It does not mean operators can ignore the updates. It simply means the most common setups dodged the bullet this time.
The Timeline That Forced Rapid Action
Researchers spotted the weak keys on October 17. The provider revoked the intermediates the next day. Microsoft blocked the authorities in a Windows update on the 20th and followed with another cleanup on the 26th. Teku shipped version 26.10.3 on the 27th. Besu had already released 26.10.2 the day before. Both removed four specific certificate roots from their Docker images: emSign ECC Root CA G3, emSign Root CA G1, emSign Root CA G2, and AAA Certificate Services.
The Docker fix is clean and automatic for anyone who pulls the latest image. Standalone binary users face extra work. They must examine their local Java installation and purge the compromised roots themselves. Anyone still on Java 26 is out of luck; that version reached end of life and will never receive the patched certificate store. Migration to Java 25 becomes mandatory.
Why Java Made the Problem Stick Around
Most modern browsers and operating systems check certificate revocation lists or use OCSP stapling. Java’s default behavior is more trusting. Once a root or intermediate sits in the trust store, Java keeps accepting certificates signed by it even after the authority has been publicly revoked. That design choice turned a fixed problem into a lingering one for Ethereum node operators.
I’ve always found the gap between theory and practice in cryptography fascinating. A key can be mathematically broken and yet still trusted by software that never bothers to look up the latest status. The Ethereum community just received a sharp reminder of that reality.
Who Needs to Update Right Now
If you run Teku or Besu inside Docker and you pull images regularly, the latest versions already protect you. Pull, restart, done. If you run the clients from binary packages or custom builds, open your Java trust store and remove the four affected roots. Confirm you are not still on an end-of-life Java release.
Operators who connect validators to external services should pay special attention. Remote beacon nodes, remote signers, MEV relays, and any HTTPS configuration endpoint sit higher on the risk list. Testnet setups that download genesis state over HTTPS also deserve a second look.
- Docker users: pull Teku 26.10.3 or Besu 26.10.2 and restart
- Binary users: update Java trust store manually
- Java 26 users: migrate to Java 25 immediately
- Anyone with external HTTPS dependencies: review mutual TLS and certificate pinning options
The advisory made clear that no successful exploitation has been observed. That is good news. It also means the window for quiet attacks is closing as more operators update. Still, the longer unpatched nodes remain online, the longer the theoretical risk exists.
Broader Context for Ethereum Infrastructure
This incident did not arrive in isolation. Earlier this month another infrastructure issue forced some validators to exit. Developers also caught and fixed a deposit-related flaw ahead of a major upgrade. The network keeps growing more complex. Complexity creates new attack surfaces. Certificate trust is only one of them.
In my view the real lesson is not about any single certificate authority. It is about the hidden dependencies that validators accumulate. Every external service, every remote signer, every HTTPS configuration download becomes a potential point of failure. Reducing those dependencies or hardening them with mutual authentication suddenly looks smarter.
Perhaps the most interesting aspect is how quickly the client teams responded once the certificate problem became public. Shipping patched Docker images within days of the Microsoft advisory shows healthy coordination. The slower part remains the long tail of operators who run older versions or custom environments.
Practical Steps Beyond the Immediate Patch
Updating is the first move. After that, a few habits can reduce future exposure. Prefer mutual TLS wherever external services are involved. Consider certificate pinning for critical connections if the client supports it. Keep Java runtimes current and monitor end-of-life dates. Review which services actually need to sit outside the local machine.
Some operators will take this opportunity to simplify. Running a beacon node and validator on the same machine eliminates several network hops. Others will double down on remote signers but add stricter authentication. Both approaches are valid. The key is intentional design rather than accidental exposure.
I’ve found that the best node operators treat security updates the way good system administrators treat kernel patches. They schedule regular checks, test in staging when possible, and refuse to let “it still works” become an excuse for staying behind.
What This Means for Everyday Stakers
Most people who stake through large providers or liquid staking protocols never touch Teku or Besu directly. Their risk is low. The people who need to care are solo stakers, small operators, and anyone running custom infrastructure. If that describes you, the updates matter.
Even if you are not affected today, the episode is worth studying. Certificate trust is one of those boring infrastructure details that suddenly becomes interesting when money is on the line. Understanding how your validator software decides which connections to trust is no longer optional knowledge.
The fact that default configurations stayed safe is a quiet win for thoughtful client design. The fact that non-default setups needed manual intervention is a reminder that convenience and security still trade off against each other.
Looking Ahead at Validator Security
Ethereum’s shift to proof of stake raised the stakes for client software quality. A bug that once might have caused a temporary fork can now move real value. The community has responded with more rigorous testing, better disclosure processes, and faster coordinated releases. This certificate incident fits that pattern.
Future improvements may include tighter default certificate handling in Java-based clients, better documentation around external service risks, and perhaps client features that make mutual authentication easier to enable. Until then the responsibility sits with operators.
One subtle opinion I hold is that the industry still under-invests in the unglamorous parts of node operation. Fancy MEV strategies and restaking products get the attention. Keeping certificate stores clean and Java versions current rarely makes headlines. Yet those boring tasks protect the rewards that make everything else possible.
The absence of reported exploitation is the best possible outcome. It suggests either that attackers never noticed the window or that the conditions required were simply too narrow. Either way, the patches close the door. Operators who update promptly keep their rewards flowing to the addresses they chose.
A Quick Checklist for Peace of Mind
- Confirm you are running Teku 26.10.3 or Besu 26.10.2 if you use Docker
- If you run binaries, inspect and clean the Java trust store
- Verify your Java version is still supported
- Review every external HTTPS dependency your validator uses
- Enable mutual TLS where practical
- Document your setup so the next update is less stressful
None of these steps is glamorous. All of them are effective. In the world of Ethereum validation, effectiveness beats glamour every single time.
The episode also highlights how interconnected the broader technology stack has become. A randomness failure at a certificate authority in one country can force urgent work by Ethereum client teams and individual node operators across the globe. That chain of dependence is both a strength of modern infrastructure and a persistent source of risk.
For those who prefer to stay deep in the details, the advisories from the client teams remain the authoritative source. They describe the exact certificates removed and the precise configurations that carried higher risk. Reading them once is worth the time.
In the end this was a contained incident handled with reasonable speed. No rewards appear to have been stolen. No mass exits were required. The network continued producing blocks. That quiet continuity is exactly what good security work aims to achieve. The operators who treat the updates as routine maintenance will sleep better. The ones who delay may discover later that “routine” was the optimistic assumption.
Staying current with client releases has always been good advice. This week it became slightly more urgent for a specific subset of the community. The difference between a near miss and a costly incident often comes down to how quickly that advice is followed.
Ethereum’s client diversity remains one of its quiet strengths. When two independent implementations surface the same external dependency problem and ship fixes within a day of each other, the system as a whole becomes more resilient. Diversity is not just about preventing consensus failures. It is also about independent teams noticing and reacting to infrastructure threats.
Looking forward, I expect more attention on the supply chain of trust that validators rely upon. Certificate authorities, Java distributions, Docker base images, and external service providers all sit inside that chain. Each link deserves periodic scrutiny. The latest patches are a concrete reminder to start that scrutiny now rather than after the next advisory lands.
For the majority of the ecosystem the story will fade quickly. For the operators who keep the lights on it becomes another item on an already long checklist. Completing that item protects both their own rewards and the broader health of the network. That dual incentive is usually enough to get the job done.
The final practical note is simple. If you have not checked your Teku or Besu version in the last few days, do it today. Pull the latest image or clean the trust store. Confirm the change. Then return to the more interesting parts of staking. The boring work is finished until the next advisory appears. And it will appear. The only question is whether your setup will already be ready.
That readiness is the real measure of operational maturity in this space. Patches will keep coming. Configurations will keep evolving. The operators who treat both as continuous responsibilities rather than occasional emergencies will keep their validators online and their rewards intact. In a network that never sleeps, that discipline is not optional. It is simply the cost of participating at the infrastructure layer.
So take the ten minutes. Run the update. Verify the certificates. Sleep a little easier knowing that one more potential path for reward redirection has been closed. The network will thank you by continuing to function exactly as designed, and your balance will reflect the difference between careful maintenance and hopeful neglect.