
What would you do if the very device meant to keep your cryptocurrency safe turned out to have something extra inside it—something no one authorized? That question stopped being theoretical this week. Ledger has confirmed that one customer’s hardware wallet contained an unauthorized electronic implant, discovered while the company investigated a wave of theft claims tied to devices sold through a Southeast Asian reseller. Estimates of the losses now sit in the tens of millions, with some on-chain researchers pointing to figures approaching or even exceeding ninety million dollars. The story is still unfolding, but the confirmation of physical tampering has already forced a hard look at how hardware wallets move through the supply chain and what users can realistically check before they trust a new device with their recovery phrase.
What Ledger Actually Confirmed About the Hidden Component
On October 10, Ledger Support issued a clear statement: one of the impacted users’ devices contained an unauthorized hardware implant. The company is reaching out to those it believes may be affected and continues to investigate. Importantly, Ledger has not claimed that its own internal systems, servers, or manufacturing processes were breached. The finding is limited to physical modification of at least one device that reached a customer.
That distinction matters. A software compromise of the company would be a different kind of crisis. An implant inside a single device, or potentially more, points toward a supply-chain or distribution problem. The reseller in question, operating across Indonesia, Malaysia, and the Philippines, has already suspended sales of all hardware wallets while the probe continues. Ledger asked the distributor to pause shipments earlier, and the broader halt followed the confirmation of the implant.
I’ve followed hardware-wallet security stories for years, and physical implants have always sat in a gray zone—technically possible, rarely confirmed in the wild at this scale. Seeing Ledger itself acknowledge one changes the conversation. The company has not released the exact model of the affected wallet, nor has it described the precise function of the component. That silence is deliberate and, for now, understandable. Investigators still need to determine whether the implant was capable of capturing the recovery phrase during setup or whether it served another purpose.
How the First Reports Emerged
Complaints began circulating on October 9. Customers who had purchased devices through the reseller reported unauthorized transactions. Ledger opened an investigation and requested that the distributor stop selling and shipping its products. Early on-chain analysis put suspected losses above seventy million dollars, then higher. One research firm later calculated roughly ninety-two point nine million dollars moved from three hundred eleven wallets across several networks, with the largest share in USDT on TRON, followed by Bitcoin and Ethereum.
Ledger has not endorsed those numbers. The company continues to treat them as independent estimates. Still, the volume of activity and the timing of transfers have convinced many observers that attackers already controlled the private keys or seed phrases of multiple wallets. Some funds appear to have moved toward mixers, including Tornado Cash, while a portion of USDT was reported frozen in linked addresses.
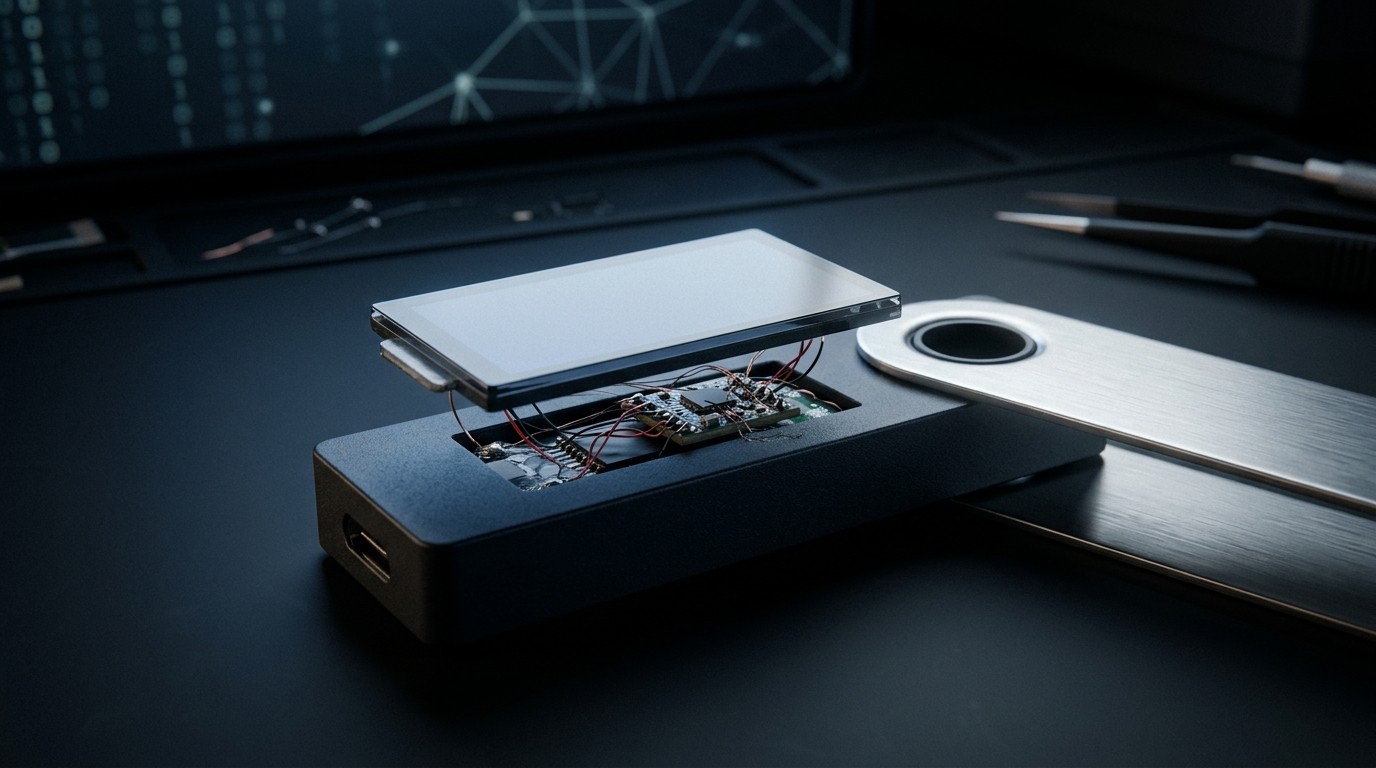
Before Ledger’s official confirmation, a well-known security researcher examined a suspicious Nano X obtained in Malaysia. He found additional electronics tucked behind the screen, inside the protective material that normally sits under the display. The packaging looked intact. That detail is unsettling. If a modified device can arrive looking factory-sealed, visual inspection alone may not be enough for the average buyer.
What the Implant Might Have Been Designed to Do
Technical analysis shared by independent researchers described a microcontroller, cellular communication hardware, and connections to the screen’s data lines. The suggestion is that a component sitting on those lines could intercept information shown during the initial setup process. A standard recovery phrase consists of twenty-four words. Anyone who obtains those words can recreate the wallet elsewhere and move the funds without ever touching the original device again.
Ledger has not confirmed that the implant it found performed this function. The company only verified the presence of unauthorized hardware. That gap between confirmation of tampering and confirmation of method is important. Assumptions can race ahead of evidence, and in security work that often creates more confusion than clarity.
In my view, the most practical takeaway is not the exact wiring diagram of one implant. It is the reminder that physical access—especially during distribution—remains a meaningful attack surface. Hardware wallets are designed to protect against remote threats and malware on a computer. They are less prepared for an adversary who can open the case, insert extra circuitry, and reseal the unit before it reaches the customer.
Advice Ledger Issued to Customers
For anyone who bought a device through the affected reseller and has not yet set it up, the guidance is straightforward: do not initialize it. Wait for further communication from Ledger. For those who already used the device, the company recommends moving funds to a new hardware wallet generated with an entirely fresh recovery phrase. Simply restoring the old phrase onto a replacement device would not solve the problem if that phrase was already exposed.
This point is worth emphasizing. Many users treat the recovery phrase as something that can be reused indefinitely across devices. In a normal scenario that works. When the integrity of the original device is in doubt, the phrase itself becomes the vulnerability. Generating a new seed and transferring assets is the only clean break.
Ledger also reminded customers that its support staff will never ask for the twenty-four-word phrase. That warning is not new, yet it gains urgency whenever a high-profile incident hits the news. Phishing sites and fake support accounts tend to surge in the days that follow. Some recent malicious advertisements have already tried to direct users to imitation Ledger pages. Those campaigns are not necessarily connected to the hardware incident, but they exploit the same moment of heightened anxiety.
The Reseller’s Response and Ownership Questions
The reseller suspended its entire hardware-wallet inventory, not just Ledger products. That broader pause suggests caution rather than an admission of fault. Former executives of the company stated that they had transferred operational control earlier in the year after an ownership change. Their statement does not prove or disprove any connection to the modified devices, but it does illustrate how complicated the distribution chain can become once products leave the manufacturer.
Supply-chain integrity has always been a quiet concern in the hardware-wallet world. Manufacturers ship to authorized resellers, who may themselves work with regional distributors or local shops. Each handoff adds a potential point of intervention. Most of the time those handoffs are routine. Occasionally they are not.
Ledger has said it is developing additional protections against physical tampering. No release date or technical details have been shared. That is typical at this stage of an investigation. The company is also working with law enforcement and has acknowledged assistance from an industry incident-response group. Researchers with relevant information are encouraged to contact the firm’s security team through its official channels.
On-Chain Estimates and What They Suggest
Independent blockchain analytics painted a picture of coordinated movement. One firm identified three hundred eleven wallets and calculated approximately ninety-two point nine million dollars in total value transferred. The largest slice involved USDT on the TRON network, followed by Bitcoin and Ethereum. Timing analysis showed clusters of activity that looked more like an attacker with preexisting control than a series of opportunistic hacks.
Later reporting noted additional Ether moved toward mixing services. A portion of the USDT was reportedly frozen. These figures remain estimates. Ledger has not verified the total, the number of victims, or the precise path of every transaction. Still, the scale is large enough that the industry cannot treat the episode as an isolated consumer complaint.
When funds leave a wallet that was supposed to be protected by a hardware device, the first questions are always the same: was the seed phrase compromised at generation, was the device itself altered, or did the user fall for a separate phishing attack? The confirmed implant answers one of those questions for at least one case. It does not yet answer how many other devices may carry similar modifications, or whether every reported loss traces back to the same method.
Why Physical Tampering Is Harder to Spot Than Software Attacks
Most crypto users worry about malware on their computers, fake browser extensions, or phishing emails. Hardware wallets were invented largely to move the private keys offline and out of reach of those threats. The assumption is that if the device itself is genuine and unopened, the recovery phrase generated on it stays secure.
An implant that sits between the secure element and the display challenges that assumption. If the screen is showing the recovery words, and extra circuitry can read the data lines feeding the display, the phrase can be captured without the user ever typing it into a computer. The packaging can look pristine. The device can pass a basic visual check. Only a careful teardown or specialized testing would reveal the extra board.
Earlier security research from the manufacturer itself had already explored scenarios in which an attacker with physical access modifies a wallet. Those discussions were theoretical or limited in scope. The current incident moves the conversation from possibility to confirmed occurrence, at least for one unit.
I find the packaging detail particularly concerning. If a modified device can travel through normal shipping channels and arrive looking factory-sealed, then the usual advice—“buy only from official sources and check the seal”—may not be sufficient in every case. Official sources remain the safest route, of course. But the industry may need stronger anti-tamper features that are visible or verifiable by the end user without specialized tools.
Practical Steps Users Can Take Right Now
Anyone who purchased a hardware wallet through the affected reseller should follow the manufacturer’s current guidance: do not set up an unused device, and consider moving funds from any already-initialized device to a new wallet with a fresh seed. Use only official support channels. Never share the recovery phrase with anyone claiming to be support staff.
For the broader community, a few habits remain worth reinforcing.
- Prefer purchasing directly from the manufacturer or its verified partners whenever possible.
- Inspect packaging carefully, even if the risk of sophisticated resealing exists.
- Generate the recovery phrase in a private setting and never photograph or store it digitally.
- Treat any unexpected request for the seed phrase as a red flag, regardless of the source.
- Keep firmware updated through official applications only.
These steps will not eliminate every risk, but they reduce the surface area an attacker can exploit. In the current climate, reducing surface area is the realistic goal.
What This Incident Reveals About Trust in Hardware
Hardware wallets occupy a special place in the crypto ecosystem. They are sold as the last line of defense for serious holdings. When that defense is shown to be vulnerable to physical intervention during distribution, the psychological impact can be larger than the number of confirmed implants. Users begin to wonder whether every device on the secondary market, or even some primary-market units, could carry hidden modifications.
Ledger’s statement that its own infrastructure remains uncompromised is meant to contain that anxiety. The company is treating the problem as localized to certain distributed units rather than a systemic manufacturing failure. Independent researchers will continue to examine devices and transaction patterns. Law enforcement involvement suggests the investigation will not remain purely technical.
Perhaps the most interesting aspect is how quickly the community moved from reports of theft to physical examination of hardware. That speed reflects both the seriousness of the losses and the maturity of on-chain analysis tools. Ten years ago, tracing ninety million dollars across multiple chains and identifying clusters of related wallets would have taken far longer. Today it happens in hours.
Looking Ahead: Stronger Anti-Tamper Measures
Ledger has indicated it is preparing additional protections against unauthorized physical modifications. Without details, it is hard to judge how effective those measures will be. Possibilities range from improved sealing techniques and holographic indicators to internal sensors that detect case opening or extra components. Some manufacturers already experiment with secure elements that refuse to operate if certain integrity checks fail. Wider adoption of such features would raise the cost of a successful implant attack.
In the meantime, the practical advice remains conservative. Buy from the most direct channel available. Verify the device through official firmware and apps. Generate seeds offline and store them offline. Move large holdings only after confirming the integrity of the new device. And treat any sudden wave of theft reports linked to a specific reseller as a reason to pause and reassess.
The confirmation of a single unauthorized implant does not mean every hardware wallet is compromised. It does mean the threat model must include sophisticated physical intervention at the distribution stage. For users who treat their seed phrase as the ultimate secret, that reminder arrives at a costly moment for those already affected.
Balancing Caution Without Panic
Security incidents in crypto often produce two extreme reactions: total dismissal or complete panic. Neither helps. The measured response is to update the mental model of risk, follow the specific guidance issued by the manufacturer, and continue using hardware wallets with eyes open about their limits. No single device or process is perfect. Layered security—hardware plus careful seed management plus official channels—still outperforms keeping large amounts on exchanges or hot wallets for most long-term holders.
I’ve found that the users who fare best after these events are the ones who already treated the recovery phrase as sacred and who avoided gray-market or unverified resellers. Those habits do not guarantee immunity, but they shrink the set of ways an attacker can reach the funds.
As the investigation continues, more details will emerge. Additional devices may be examined. Transaction graphs will be refined. Attribution, if it arrives at all, will take time. For now, the confirmed fact is simple and serious: at least one customer received a hardware wallet containing electronics that did not belong there. That fact alone justifies the heightened attention the story has received.
Final Thoughts on Protecting What Matters
Cryptocurrency self-custody is empowering precisely because it removes intermediaries. That power comes with responsibility. Hardware wallets remain one of the strongest tools available for exercising that responsibility, yet they are not magic. They depend on an intact supply chain, careful user behavior, and ongoing vigilance from manufacturers.
The current episode underscores the need for all three. Users should stay informed through official channels, follow the concrete steps outlined for affected devices, and resist the urge to share seed phrases with anyone under any circumstances. Manufacturers will need to keep raising the bar on physical security features. And the broader ecosystem will continue refining its ability to detect and respond when something goes wrong.
In the end, the goal is not perfect safety—an unrealistic standard in any open system—but a practical reduction of the most likely and most damaging attack paths. The discovery of an unauthorized implant inside a customer device is a clear signal that physical tampering during distribution belongs on that list of paths. Addressing it will take time, transparency, and continued scrutiny from both the company and independent researchers. For everyone holding crypto on hardware, the immediate task is simpler: protect the recovery phrase as if the device itself might not be entirely trustworthy, because in at least one documented case, it was not.