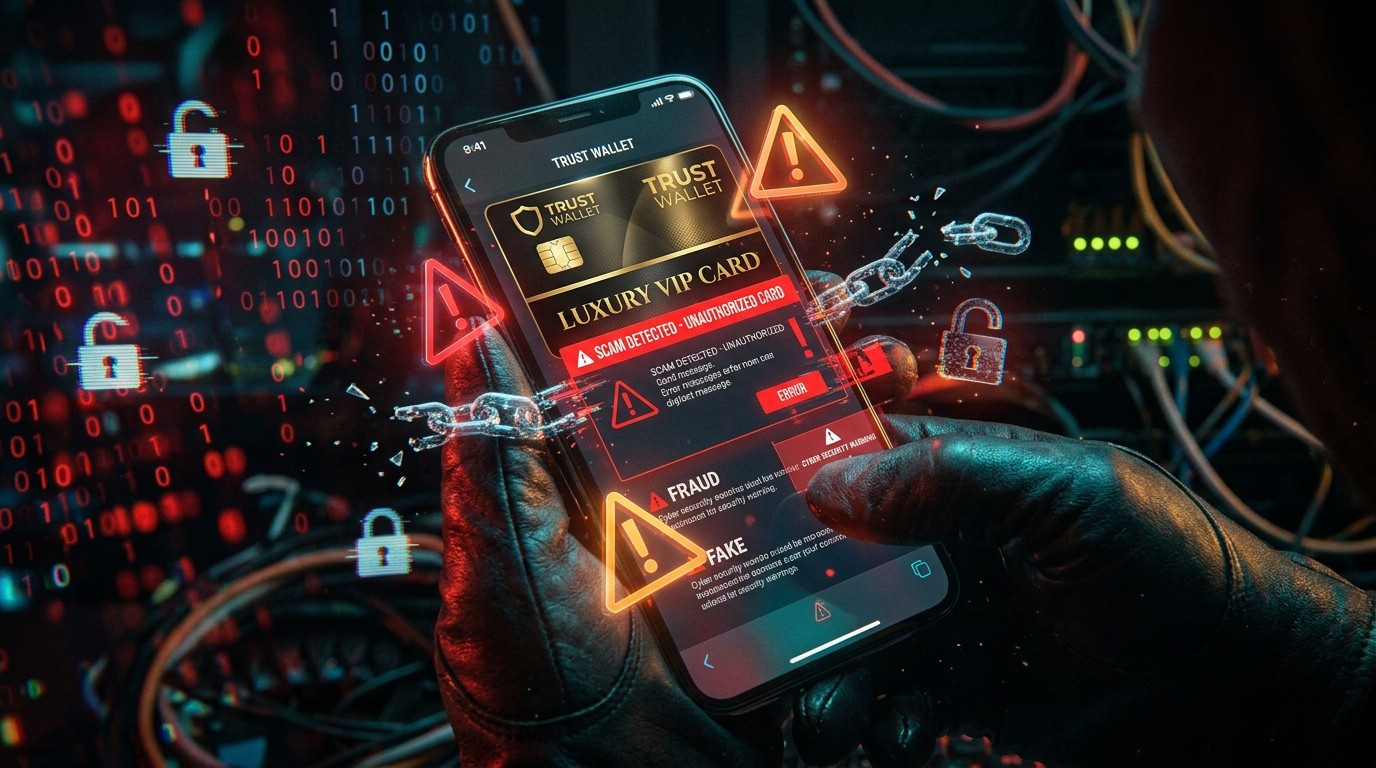

Have you ever scrolled past an offer that looked almost too perfect and thought, just for a second, that maybe this time it was real? I have. And that exact feeling is what scammers count on. Right now a polished website is circulating that claims to offer a premium cryptocurrency payment card under the Trust Wallet name. It promises a $100,000 spending limit, up to 8% cashback, no identity checks, airport lounge access, and a metal card for a single dollar. It looks official. It uses familiar branding. And according to the company’s own security team, every part of it is fake.
How This Fake Crypto Card Scheme Actually Works
The site does not simply ask for money up front in an obvious way. Instead it invites users to connect their cryptocurrency wallets as the first step toward receiving the card. That single action is where the real risk begins. A wallet connection by itself does not always move funds, yet it opens the door for follow-up signature requests that can grant spending permissions over tokens. Once those permissions are approved, an attacker-controlled contract can drain assets without ever needing the recovery phrase.
Security researcher accounts first highlighted the site after noticing the aggressive marketing and the use of Trust Wallet’s visual identity. The promotional material showed three membership levels labeled Lite, Signature, and Metal. Each level carried higher cashback percentages and extra perks. The highest tier claimed 8% rewards, unlimited lounge access, and round-the-clock concierge service. All of it was available, the site insisted, with no Know Your Customer process and for a $1 issuance fee.
James Bro, speaking for Trust Wallet’s security team, responded directly and stated that the website has no connection to the company. Legitimate products and services, he noted, appear only inside the official application and on the verified domain. Anything else that asks users to approve wallet connections or signatures for a payment card should be treated as hostile.
Why the Offer Looks So Convincing
Scammers have become skilled at copying design language. They borrow logos, color schemes, and even the tone of official announcements. In this case the site claimed licenses in multiple countries and presented the card as a seamless way to spend digital assets anywhere, complete with Apple Pay and Google Pay support plus zero foreign-exchange fees. Those details make the pitch feel institutional rather than amateur.
I’ve watched similar campaigns appear over the past couple of years. Fake applications showed up on third-party app stores. Cloned websites advertised airdrops or exclusive cards. Each time the pattern repeats: attractive numbers, urgency, and a request to connect a wallet. The current campaign simply raises the stakes by promising benefits that sound almost institutional.
Legitimate Trust Wallet offerings are available through its official channels. Users should never connect wallets or approve suspicious requests in order to obtain a payment card.
That statement from the security team is clear. Still, many people will encounter the site through social media shares or search results and may not see the warning first. That is why understanding the mechanics matters more than simply knowing one particular domain is fraudulent.
The Real Danger Behind Wallet Connections
Connecting a wallet to an unknown site is not automatically catastrophic, yet it creates an opportunity. Attackers often follow the connection with carefully worded transaction requests. Those requests can look like routine approvals or token listings. In reality they may grant unlimited spending allowances on specific assets. Once the signature is given, the contract can move tokens at any time without further interaction from the owner.
Recent incidents illustrate the point. One Ethereum user lost nearly a million dollars after approving a malicious transaction. Another case involved roughly $1.65 million drained after a victim signed a smart-contract interaction on a fraudulent exchange site. Security researchers have also linked large unauthorized withdrawals to permit signatures that effectively handed control of tokens to outsiders. In each situation the private keys stayed with the victim; the permissions did the damage.
Perhaps the most interesting aspect is how ordinary the process can appear. The site never asks for the seed phrase. It simply presents a series of clicks that feel like onboarding. That psychological design is deliberate. People who would never type their recovery words into a random form will still approve a transaction if it looks like part of a legitimate service.
Red Flags That Should Stop You Immediately
Certain warning signs appear again and again. An unusually high spending limit combined with almost no verification is one. A $1 issuance fee for a metal card and premium benefits is another. Claims of licenses in multiple jurisdictions without easily verifiable documentation should raise questions. Any site that uses a well-known brand’s name and logo while directing users to connect wallets outside the official application deserves extreme caution.
- Offers that require wallet connection before any real identity or eligibility check
- Cashback percentages that exceed typical industry ranges without clear funding sources
- Pressure to act quickly or limited-time language around card issuance
- Absence of clear company registration details or verifiable support channels
- Branding that closely copies a major wallet provider but lives on a different domain
I tend to treat any combination of these elements as a hard stop. Even if the site looks polished, the risk-reward calculation rarely favors the user.
What Trust Wallet Actually Offers Versus the Fake Version
The legitimate company has never promoted a $100,000-limit card with no KYC and an issuance fee of one dollar. Its real products and features appear inside the official mobile application and on the verified website. Users who want to explore any payment-related tools should begin there and nowhere else. Downloading software from third-party stores or connecting to promotional domains that merely look official has already caused problems in the past.
In earlier incidents the company publicly asked platforms to remove counterfeit applications. Those cases involved fake versions of the wallet itself rather than a payment card, yet the underlying method remained the same: borrow trust, then extract permissions or credentials. The current campaign simply updates the packaging.
Practical Steps to Protect Your Assets Right Now
Protecting a wallet starts with habit rather than tools. Before connecting to any new site, pause and verify the domain character by character. Bookmark the official application and website so you never rely on search results or shared links. When a transaction request appears, read the details carefully. If the request asks for unlimited token approvals or spending permissions that seem unrelated to the stated purpose, reject it.
Hardware wallets add an extra layer because they keep private keys offline and require physical confirmation for each signature. Even then, the human decision remains critical. Approving a malicious permit on a hardware device still grants the attacker the same spending rights. The device simply makes the approval process more deliberate.
Another useful practice is to maintain separate wallets for different activities. A small hot wallet for experimentation and daily use can sit alongside a larger cold-storage setup that never interacts with experimental sites. That separation limits the damage if one address is compromised.
- Verify every domain and never rely on links from social media alone
- Read every transaction request in full before signing
- Revoke unused token approvals periodically through trusted tools
- Keep the majority of holdings in cold storage that does not browse the web
- Treat any offer that combines high rewards with zero verification as suspicious by default
How Scammers Keep Evolving Their Methods
The current fake-card campaign is not isolated. Attackers have previously impersonated NFT projects, exchange interfaces, and even individual developers. Each wave tests new psychological angles. Sometimes the bait is exclusivity. Sometimes it is urgency. Sometimes it is the promise of institutional-grade benefits delivered through a consumer wallet. The technical foundation stays consistent: obtain a signature that grants control over assets.
In my experience the most effective defense is skepticism applied early. Once a wallet is connected and a malicious permit is signed, recovery becomes difficult and often incomplete. Prevention is far simpler than cleanup. That is why public warnings from security teams matter. They interrupt the momentum of a campaign before more people click through.
Still, warnings alone are never enough. New domains appear daily. Branding is copied within hours. The only sustainable approach is to treat every unsolicited offer of premium benefits as a potential trap until proven otherwise through official channels.
What to Do If You Already Connected
If a wallet has already interacted with the suspicious site, immediate steps can limit further loss. First, stop using the affected address for new activity. Transfer remaining assets to a fresh wallet that has never connected to the fraudulent domain, preferably through a hardware device. Then review and revoke any active token approvals that may have been granted. Several blockchain explorers and specialized tools allow users to inspect and cancel those permissions.
Reporting the incident to the wallet provider and relevant authorities can also help. Even if individual recovery is unlikely, the information feeds broader efforts to take down domains and alert other users. Document everything: screenshots, transaction hashes, and the exact sequence of actions. That record becomes useful if investigators later identify the operators.
Emotional reactions are normal. Feeling foolish after approving a malicious request is common. The important point is to act quickly rather than freeze. Assets still sitting in the compromised wallet remain at risk until they are moved and permissions are cleared.
Broader Lessons for Everyday Crypto Users
This episode reinforces a few principles that apply far beyond one fake card. First, brand recognition is not proof of authenticity. Logos and design systems can be copied. Second, extraordinary benefits usually require ordinary verification. An offer that skips identity checks while promising high spending limits and premium services is almost always structured to extract value rather than deliver it. Third, wallet permissions are powerful. Treating them casually is the digital equivalent of handing someone a signed blank check.
I’ve found that the users who stay safest are the ones who slow down. They double-check domains. They read the fine print on every signature request. They keep most of their holdings offline. None of those habits is complicated, yet each one reduces exposure dramatically.
The technology itself is not the enemy. Smart contracts and permission systems enable useful products. The problem arises when those systems are abused by people who understand human psychology better than most users understand blockchain mechanics. Closing that knowledge gap is the practical response.
Looking Ahead: Staying One Step Ahead of the Next Campaign
New variations will appear. Some will advertise different rewards. Others will impersonate other well-known brands. The core request will remain the same: connect the wallet and approve a signature. Recognizing that pattern is more valuable than memorizing any single fraudulent domain.
Communities that share warnings quickly help reduce the damage. When researchers flag a site and the affected company confirms the fraud, the information spreads faster than the scam itself. That collective response is one of the few advantages users hold.
Ultimately the responsibility sits with each individual holder. No company can police every corner of the internet. No warning can reach every potential victim in time. The decision to connect or to walk away is personal. Making that decision with clear eyes is the difference between keeping assets and watching them disappear.
The fake Trust Wallet card campaign is a reminder that attractive packaging does not equal legitimacy. A $100,000 limit, 8% cashback, and a metal card for one dollar sound appealing until the cost becomes the entire contents of a wallet. Official channels exist for a reason. Using them consistently is still the most reliable protection available. Stay skeptical, read every request, and treat any offer that feels too perfect as a signal to pause rather than proceed.